Short answer: Two critical flaws in Langflow could let attackers run code on servers without an account. Users should upgrade to version 1.13.0 and disable auto-login.
TL;DR
- Two critical flaws in Langflow could let attackers run code.
- Users should upgrade to version 1.13.0.
- Disable auto-login for added security.
- Check for updates and patch vulnerabilities.
What is CVE-2026-104339?
Langflow is a software tool with two critical flaws that allow attackers to run code on servers without needing an account. These vulnerabilities, identified as CVE-2026-104339 and CVE-2026-110186, can be exploited by unauthenticated attackers. To mitigate these risks, users should update to the latest version and disable auto-login features to enhance security.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 02 Nov 2026 |
| CVE | CVE-2026-104339 |
| CVSS | 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-94 (code injection) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | www.ibm.com |
| CVE | CVE-2026-110186 |
| CVSS | 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-94 (code injection) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | www.ibm.com |
| CVE | CVE-2026-110192 |
| CVSS | 6.5 MEDIUM CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N |
| Weakness | CWE-522 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | www.ibm.com |
| Affected product | IBM Langflow |
| Published in NVD | 2026-10-29 (CVE-2026-104339) |
| Published in NVD | 2026-10-29 (CVE-2026-110186) |
| Published in NVD | 2026-10-29 (CVE-2026-110192) |
How it works
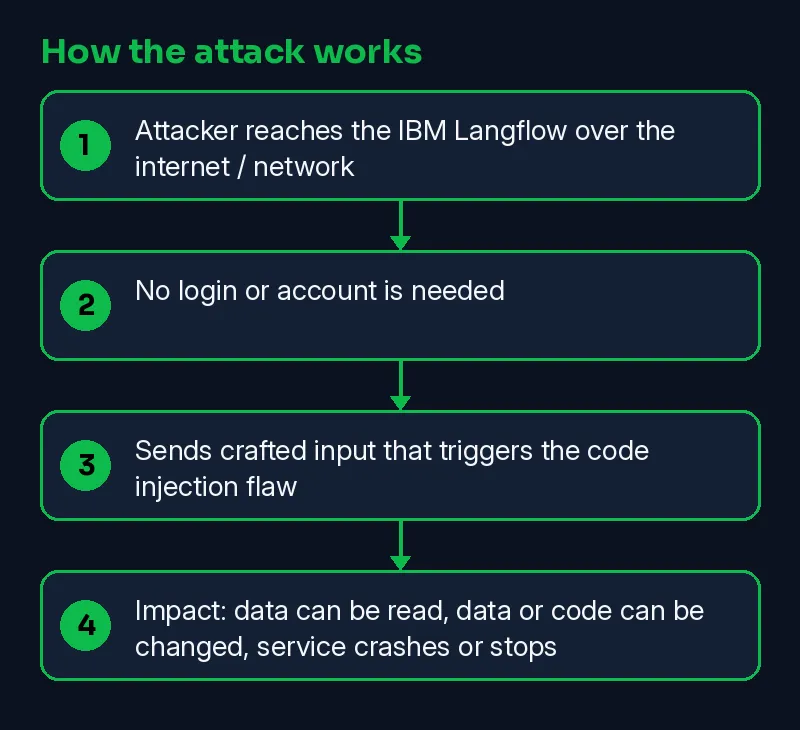
Langflow is an open-source tool for building AI models. A security flaw lets attackers run code on servers without needing to log in. Another flaw lets attackers execute code even if they aren't logged in. Both flaws are critical and can be exploited by unauthenticated attackers.
- Attacker reaches the IBM Langflow over the internet / network
- No login or account is needed
- Sends crafted input that triggers the code injection flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-10-29 | CVE-2026-104339 published in NVD | NVD |
| 2026-10-29 | CVE-2026-110186 published in NVD | NVD |
| 2026-10-29 | CVE-2026-110192 published in NVD | NVD |
| 2026-11-02 | Reported by The Hacker News | The Hacker News |
| 2026-11-03 | This Skillmate explainer published | Skillmate |
How to fix it
- Update IBM Langflow to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-104339 and upgrade to the fixed release it lists.
- Read the vendor advisory for CVE-2026-110186 and upgrade to the fixed release it lists.
- Read the vendor advisory for CVE-2026-110192 and upgrade to the fixed release it lists.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-104339 is a real NVD record scored 9.8 CRITICAL | CISA KEV does not list CVE-2026-104339 as exploited in the wild |
| CVE-2026-110186 is a real NVD record scored 9.8 CRITICAL | CISA KEV does not list CVE-2026-110186 as exploited in the wild |
| CVE-2026-110192 is a real NVD record scored 6.5 MEDIUM | CISA KEV does not list CVE-2026-110192 as exploited in the wild |
| Reported by The Hacker News | |
| Reported by www.ibm.com | |
| Reported by docs.langflow.org |
Why it matters
These flaws pose significant risks to companies and users. They can lead to data breaches, service disruption, and loss of sensitive information.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is Langflow?
Langflow is a software tool that developers use to create and manage workflows. It has some security flaws that could let attackers run code on servers.
How serious are these vulnerabilities?
The vulnerabilities are critical, with a CVSS score of 9.8, meaning they could allow attackers to run code on the server without needing to log in.
Are there any known false positives for these vulnerabilities?
Yes, a false positive could occur if a legitimate user tries to log in multiple times, thinking they forgot their password.
Related Skillmate posts
Sources
- Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers (The Hacker News)
- Primary source / advisory (www.ibm.com)
- Vendor advisory CVE-2026-104339 (www.ibm.com)
- Vendor advisory CVE-2026-110186 (www.ibm.com)
- Langflow (primary source) (docs.langflow.org)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.