Short answer: A critical bug called HTTP2Shell was found in Brotli, a compression library. Users of Node.js, Bun, Envoy, and Python are affected. Update to the latest version or use virtual patching.
TL;DR
- Critical bug found in Brotli (HTTP2Shell).
- Affects Node.js, Bun, Envoy, and Python.
- Update to latest versions.
- Use virtual patching if updates are delayed.
What is CVE-2026-111497?
HTTP2Shell is a serious security flaw in Brotli, a compression library. Attackers can exploit it to run their own code on your system. This bug is critical and has been actively used by attackers. Software developers need to update their libraries to the latest versions or use virtual patching to protect their applications until updates are available.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | Help Net Security |
|---|---|
| Date reported | 03 Nov 2026 |
| CVE | CVE-2026-111497 |
| CVSS | 9.2 CRITICAL CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-252 (see NVD), CWE-787 (out-of-bounds write) |
| CISA KEV | Yes, added 2026-10-27; federal due date 2026-11-10 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | github.com |
| Affected product | Google Brotli |
| Published in NVD | 2026-10-22 (CVE-2026-111497) |
How it works
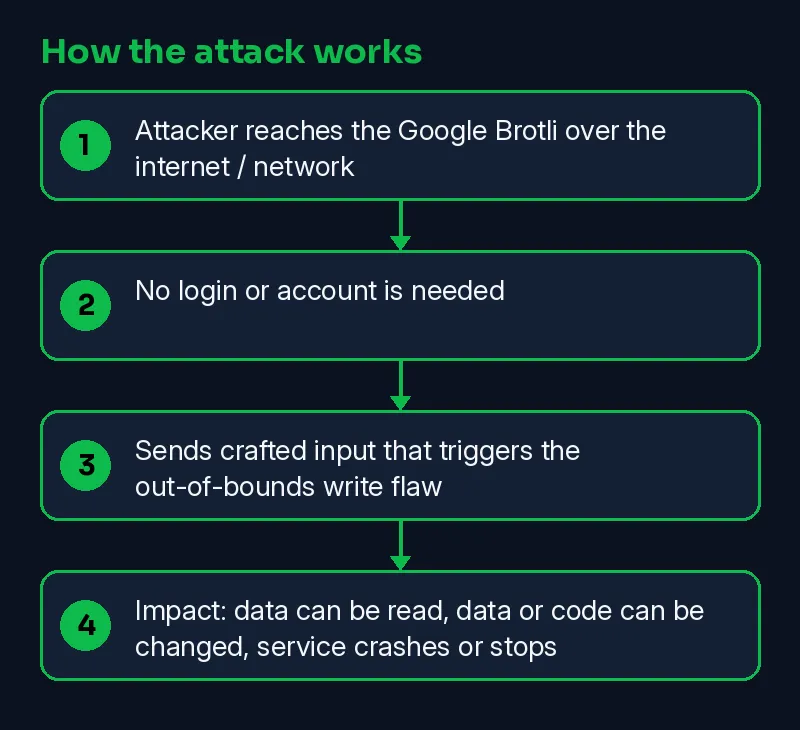
HTTP2Shell is a bug in Brotli, a compression library used in Node.js, Bun, Envoy, and Python. It can let attackers run code on your server without fixing the bug. Sweet Virtual Patching watches your running application and blocks the attack, giving you time to patch it properly.
- Attacker reaches the Google Brotli over the internet / network
- No login or account is needed
- Sends crafted input that triggers the out-of-bounds write flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-10-22 | CVE-2026-111497 published in NVD | NVD |
| 2026-10-27 | CVE-2026-111497 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-03 | Reported by Help Net Security | Help Net Security |
| 2026-11-03 | This Skillmate explainer published | Skillmate |
| 2026-11-10 | US federal agencies must patch by this date | CISA KEV |
How to fix it
- Update Google Brotli to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-111497 and upgrade to the fixed release it lists.
- CVE-2026-111497 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Watch for crashes or unauthenticated remote code execution.
What is confirmed
- CVE-2026-111497 is a real NVD record scored 9.2 CRITICAL
- CISA lists CVE-2026-111497 as exploited in the wild
- Reported by Help Net Security
- Reported by github.com
Why it matters
HTTP2Shell shows why fixing bugs takes time, while attackers can exploit them quickly. This matters because it highlights the need for virtual patching to protect against attacks while waiting for fixes. Companies and users need to be aware to protect their systems.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is Brotli?
Brotli is a compression library that reduces file size, used in web servers and applications.
How does Sweet Virtual Patching work?
Sweet Virtual Patching uses AI to monitor and block attacks in real-time without changing code.
What is HTTP2Shell?
HTTP2Shell is a remote code execution flaw in Brotli, allowing attackers to execute code without permission.
How can I protect against this vulnerability?
Update Brotli libraries to the latest version and use virtual patching to mitigate risks.
Related Skillmate posts
Sources
- Product showcase: Sweet Virtual Patching stops HTTP2Shell while fixes catch up (Help Net Security)
- Vendor advisory CVE-2026-111497 (github.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.