Short answer: Synology warns of C3RB3R ransomware attacks targeting outdated DSM versions. Update immediately to avoid data loss.
TL;DR
- Synology issued a warning.
- C3RB3R ransomware targets outdated systems.
- Update DSM to protect data.
- Enable automatic updates for future security.
What is CVE-2021-22205?
C3RB3R ransomware attacks target outdated Synology DiskStation Manager (DSM) versions. These attacks encrypt data and demand ransom. To protect your data, update your DSM to the latest version and enable automatic updates. Synology advises immediate action to avoid data loss and system compromise.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Ransomware
- Malware that locks or steals files and demands money to give them back.
Key facts
| Reported by | BleepingComputer |
|---|---|
| Date reported | 02 Nov 2026 |
| CVE | CVE-2021-22205 |
| CVSS | 10.0 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Weakness | CWE-94 (code injection) |
| CISA KEV | Yes, added 2021-11-03; federal due date 2021-11-17 |
| Ransomware use | Known (CISA KEV) |
| Vendor advisory | gitlab.com |
| CVE | CVE-2021-26084 |
| CVSS | 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-917 (see NVD) |
| CISA KEV | Yes, added 2021-11-03; federal due date 2021-11-17 |
| Ransomware use | Known (CISA KEV) |
| Vendor advisory | jira.atlassian.com |
| CVE | CVE-2023-22518 |
| CVSS | 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-863 (incorrect authorization) |
| CISA KEV | Yes, added 2023-11-07; federal due date 2023-11-28 |
| Ransomware use | Known (CISA KEV) |
| Vendor advisory | confluence.atlassian.com |
| Affected product | GitLab Community and Enterprise Editions |
| Fixed versions | 7.4.11 (CVE-2021-26084, per NVD) |
| Published in NVD | 2021-04-23 (CVE-2021-22205) |
| Published in NVD | 2021-08-30 (CVE-2021-26084) |
| Published in NVD | 2023-10-31 (CVE-2023-22518) |
How it works
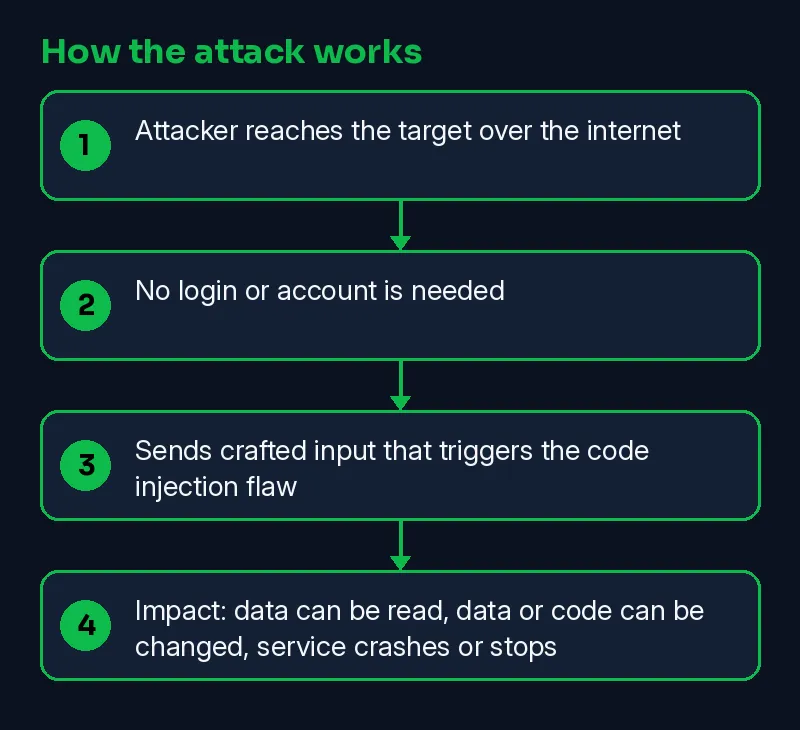
Vulnerability CVE-2021-26084 lets attackers run code, and CVE-2023-22518 lets them change admin settings.
- Attacker reaches the target over the internet
- No login or account is needed
- Sends crafted input that triggers the code injection flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
Timeline
| Date | Event | Source |
|---|---|---|
| 2021-04-23 | CVE-2021-22205 published in NVD | NVD |
| 2021-08-30 | CVE-2021-26084 published in NVD | NVD |
| 2021-11-03 | CVE-2021-22205 added to CISA KEV (actively exploited) | CISA KEV |
| 2021-11-03 | CVE-2021-26084 added to CISA KEV (actively exploited) | CISA KEV |
| 2021-11-17 | US federal agencies must patch by this date | CISA KEV |
| 2023-10-31 | CVE-2023-22518 published in NVD | NVD |
| 2023-11-07 | CVE-2023-22518 added to CISA KEV (actively exploited) | CISA KEV |
| 2023-11-28 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-02 | Reported by BleepingComputer | BleepingComputer |
| 2026-11-03 | This Skillmate explainer published | Skillmate |
How to fix it
- Update GitLab Community and Enterprise Editions now. NVD lists the fixed versions as 7.4.11.
- Read the vendor advisory for CVE-2021-22205 and upgrade to the fixed release it lists.
- CVE-2021-22205 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2021-26084 and upgrade to the fixed release it lists.
- CVE-2021-26084 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2023-22518 and upgrade to the fixed release it lists.
- CVE-2023-22518 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
What is confirmed
- CVE-2021-22205 is a real NVD record scored 10.0 CRITICAL
- CISA lists CVE-2021-22205 as exploited in the wild
- CVE-2021-26084 is a real NVD record scored 9.8 CRITICAL
- CISA lists CVE-2021-26084 as exploited in the wild
- CVE-2023-22518 is a real NVD record scored 9.8 CRITICAL
- CISA lists CVE-2023-22518 as exploited in the wild
- NVD lists fixed versions for CVE-2021-26084: 7.4.11
- Reported by BleepingComputer
- Reported by www.synology.com
- Reported by jira.atlassian.com
- Reported by confluence.atlassian.com
Why it matters
Vulnerabilities can lead to data loss and ransom demands. Companies and users must update systems to avoid attacks, protecting data and reducing risks.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What are the affected versions of Confluence?
Confluence versions before 6.13.23, 6.14.0 to 7.4.10, 7.5.0 to 7.11.5, and 7.12.0 to 7.12.4 are affected.
What should I do if I find signs of compromise?
Immediately patch to the latest version and review security logs for unauthorized access attempts.
Are there any temporary mitigations for Confluence?
Yes, block access to certain endpoints and modify web.xml to add security constraints.
Sources
- Synology warns of C3RB3R ransomware attacks targeting NAS devices (BleepingComputer)
- Primary source / advisory (www.synology.com)
- Vendor advisory CVE-2021-26084 (jira.atlassian.com)
- Vendor advisory CVE-2023-22518 (confluence.atlassian.com)
- Synology (primary source) (www.synology.com)
- Vendor advisory CVE-2021-22205 (gitlab.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.