Short answer: Attackers are exploiting a flaw in the CryptoPayment Gateway WordPress plugin, which can expose wallet credentials. Site owners should remove the plugin and rotate wallet keys to stay safe.
TL;DR
- Unpatched CryptoPayment Gateway version 1.2.1-2 is vulnerable.
- The vulnerability has a CVSS score of 10.0, indicating critical severity.
- Plugin has been removed from the WordPress Plugin Directory.
What is CVE-2026-81648?
This incident involves a security flaw in the CryptoPayment Gateway WordPress plugin, versions 1.2.1 to 1.2.2. Attackers can exploit this flaw to delete files and access sensitive wallet information. The flaw allows unauthenticated users to perform administrative tasks, making it a serious threat to users. Site owners should remove the plugin and update their wallet keys to secure their systems.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Exploit
- Code or steps that take advantage of a weakness.
- Unpatched
- No fix is available yet, or the fix has not been installed.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 03 Nov 2026 |
| CVE | CVE-2026-81648 |
| CVSS | 10.0 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Weakness | CWE-862 (missing authorization) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Affected product | CryptoPayment Gateway |
| Published in NVD | 2026-09-13 (CVE-2026-81648) |
How it works
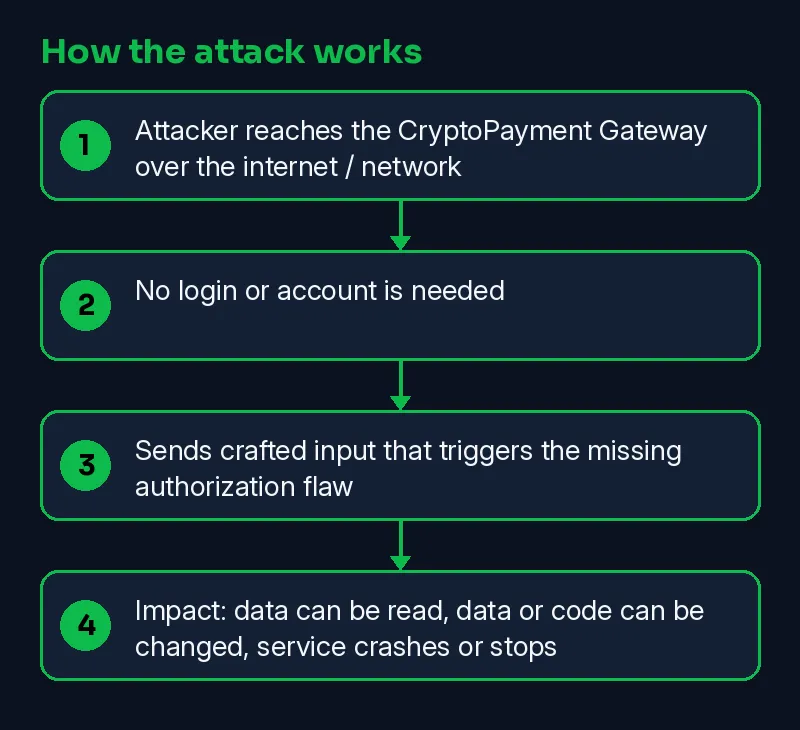
A flaw in the CryptoPayment Gateway WordPress plugin allows unauthenticated users to delete files and access sensitive data. This is because the plugin does not check if a user is authorized before performing administrative tasks.
- Attacker reaches the CryptoPayment Gateway over the internet / network
- No login or account is needed
- Sends crafted input that triggers the missing authorization flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-09-13 | CVE-2026-81648 published in NVD | NVD |
| 2026-11-03 | Reported by The Hacker News | The Hacker News |
| 2026-11-03 | This Skillmate explainer published | Skillmate |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
WordPress
WP-CLI: lists plugins and their versions:
wp plugin listWP-CLI: shows the WordPress version:
wp core versionHow to fix it
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should watch for unauthorized file deletions and changes to payment gateway settings.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-81648 is a real NVD record scored 10.0 CRITICAL | CISA KEV does not list CVE-2026-81648 as exploited in the wild |
| Reported by The Hacker News | NVD links no vendor advisory for CVE-2026-81648 yet |
Why it matters
This flaw can expose sensitive wallet data. Companies and users should remove the plugin, rotate keys, and audit sites.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is an AJAX endpoint?
An AJAX endpoint is a web service that allows for asynchronous data retrieval. Attackers can exploit it to perform unauthorized actions.
How can I protect my site from this vulnerability?
Remove the CryptoPayment Gateway plugin and update to a secure version. Rotate wallet keys and audit your site for any suspicious changes.
What is the CVSS score and what does it mean?
The CVSS score is 10.0, indicating a critical severity. It means the vulnerability is highly dangerous and needs immediate attention.
How many times was the plugin downloaded?
The plugin was downloaded 1,845 times in total, including 20 downloads in the last seven days.
Related Skillmate posts
Sources
- Attackers Target Unpatched CryptoPayment Gateway Flaw That Can Expose Wallet Credentials (The Hacker News)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.