Short answer: A critical flaw in LXD and MicroCloud lets attackers impersonate trusted clients. Update to the latest versions to fix it.
TL;DR
- LXD and MicroCloud versions before 6.10.1, 5.21.9, 5.0.11, 4.0.15, 3.4.1, 2.1.5 are affected.
- An attacker can impersonate any trusted client without the private key.
- The flaw can give root access to the host machine if the impersonated account is privileged.
- Network access to the HTTPS API and the public certificate of a trusted client are required.
- Update to the latest snap versions to fix the issue.
What is CVE-2026-112816?
This issue is a security vulnerability in Canonical's LXD and MicroCloud software. Attackers can impersonate trusted clients by using a crafted certificate chain. This means they can gain full access to clusters and virtual machines, potentially gaining root access if the impersonated account has high privileges. The flaw affects older versions of LXD and MicroCloud and can be exploited if an attacker can reach the HTTPS API and has the public certificate of a trusted client. To fix the issue, update to the latest versions available.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- CVSS score
- A 0 to 10 rating of how dangerous a weakness is. 9 or more is critical.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 01 Nov 2026 |
| CVE | CVE-2026-112816 |
| CVSS | 10.0 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-295 (improper certificate validation) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | discourse.ubuntu.com |
| Affected product | Canonical LXD and MicroCloud |
| Fixed versions | 4.0.15, 5.0.11, 5.21.9, 6.10.1 (CVE-2026-112816, per NVD) |
| Published in NVD | 2026-10-30 (CVE-2026-112816) |
How it works
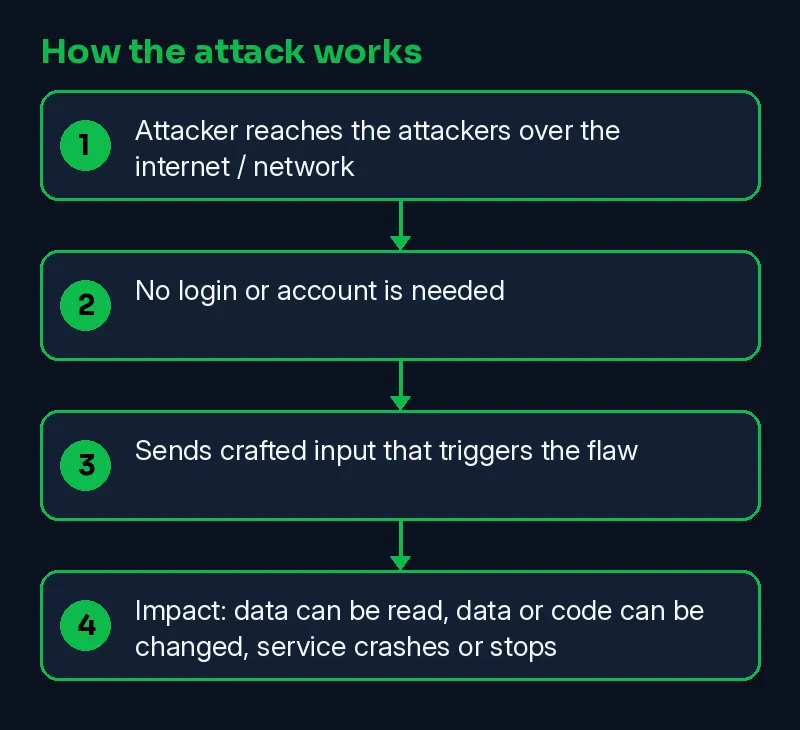
An attacker can impersonate a trusted client by appending their public certificate to a valid client's certificate chain. This works because the server only checks the first certificate in the chain for key ownership, not the rest of the chain.
- Attacker reaches the target over the internet
- No login or account is needed
- Sends crafted input that triggers the improper certificate validation flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-10-30 | CVE-2026-112816 published in NVD | NVD |
| 2026-11-01 | Reported by The Hacker News | The Hacker News |
| 2026-11-01 | This Skillmate explainer published | Skillmate |
How to fix it
- Update Canonical LXD and MicroCloud now. NVD lists the fixed versions as 4.0.15, 5.0.11, 5.21.9, 6.10.1.
- Read the vendor advisory for CVE-2026-112816 and upgrade to the fixed release it lists.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-112816 is a real NVD record scored 10.0 CRITICAL | CISA KEV does not list CVE-2026-112816 as exploited in the wild |
| NVD lists fixed versions for CVE-2026-112816: 4.0.15, 5.0.11, 5.21.9, 6.10.1 | |
| Reported by The Hacker News | |
| Reported by discourse.ubuntu.com | |
| Reported by github.com |
Why it matters
This flaw allows unauthenticated attackers to gain full access to clusters and virtual machines.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is mutual TLS?
Mutual TLS is a security method where both the client and server verify each other's identity using digital certificates.
Can this flaw be exploited remotely?
Yes, an attacker can exploit this flaw by reaching the LXD HTTPS API and having the public certificate of a trusted client.
How can I update my LXD and MicroCloud installations?
Run sudo snap refresh lxd and sudo snap refresh microcloud to update to the latest versions.
What products are affected?
LXD versions 4.0.14, 5.0.10, 5.21.8, and 6.9, and MicroCloud versions 2 and 3 are affected.
Related Skillmate posts
Sources
- CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key (The Hacker News)
- Primary source / advisory (discourse.ubuntu.com)
- Primary source / advisory (github.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.