
Short answer: China-aligned hackers hijacked Sogou Input Method to deploy DarkVigil, targeting users in Asia and Europe. Update to the latest version and use secure connections.
TL;DR
- Hackers used DNS hijacking on Sogou Input Method.
- Affected users in Hong Kong, Thailand, Japan, Vietnam, Sri Lanka, Oman.
- DarkVigil is a backdoor used for surveillance.
- Update to Sogou Input Method 16.10 or later.
- Use HTTPS for secure connections.
What is CVE-2026-120422?
China-aligned hackers hijacked the Sogou Input Method's DNS to deploy DarkVigil, a backdoor that allows remote control. They targeted users in Asia and Europe. ESET identified the attackers as SlippyNunchucks and linked them to surveillance efforts for the Chinese government. The vulnerability was fixed by updating to Sogou Input Method 16.10, which moved unencrypted requests to HTTPS.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Malware
- Harmful software made to spy, steal or damage.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 04 Nov 2026 |
| CVE | CVE-2026-120422 |
| CVSS | 8.9 HIGH CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:P/VC:H/VI:H/VA:N/SC:H/SI:H/SA:H/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:N/AU:X/R:U/V:D/RE:M/U:X |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| CVE | CVE-2026-51990 |
| CVSS | 9.8 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Weakness | CWE-94 (code injection) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Affected product | Sogou Input Method DNS |
| Published in NVD | 2026-11-04 (CVE-2026-120422) |
| Published in NVD | 2026-09-16 (CVE-2026-51990) |
How it works
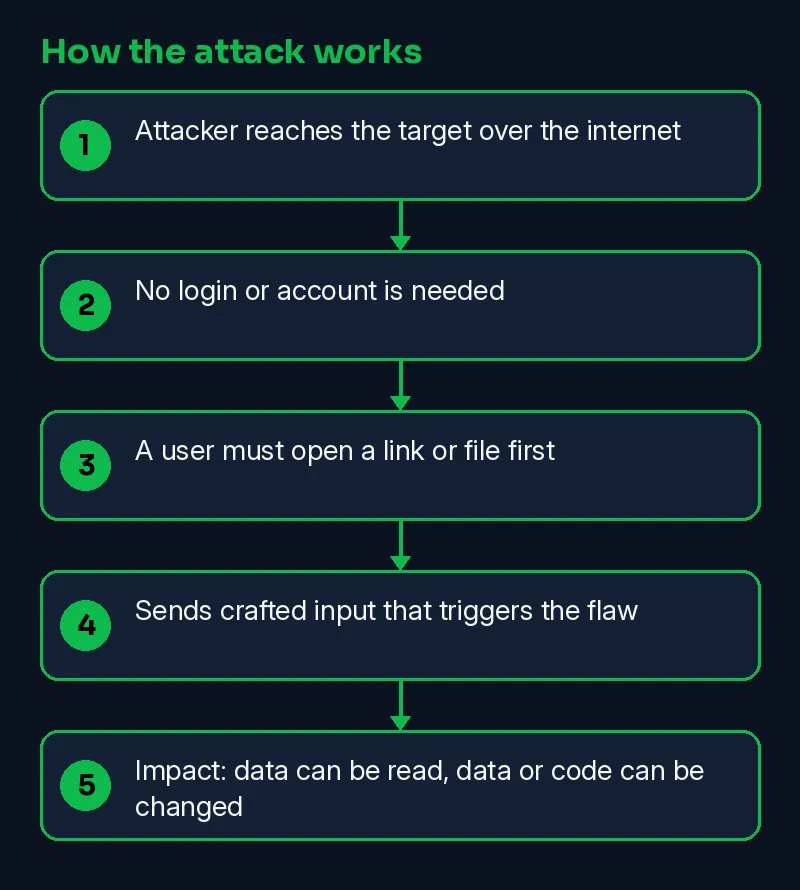
Hackers tricked Sogou Input Method by changing its DNS requests to point to their servers, delivering the DarkVigil backdoor. The app then downloaded malicious files and ran them.
- Attacker reaches the target over the internet
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the flaw
- Impact: data can be read, data or code can be changed
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-09-16 | CVE-2026-51990 published in NVD | NVD |
| 2026-11-04 | CVE-2026-120422 published in NVD | NVD |
| 2026-11-04 | Reported by The Hacker News | The Hacker News |
| 2026-11-09 | This Skillmate explainer published | Skillmate |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Microsoft Windows
PowerShell: lists the latest installed updates:
Get-HotFix | Sort-Object InstalledOn -Descending | Select-Object -First 10shows the Windows version and build:
winverHow to fix it
- Update Sogou Input Method DNS to the fixed release named in the vendor advisory.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should look for unexpected DNS requests, unexplained program launches, and unauthorized network connections.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-120422 is a real NVD record scored 8.9 HIGH | CISA KEV does not list CVE-2026-120422 as exploited in the wild |
| CVE-2026-51990 is a real NVD record scored 9.8 CRITICAL | NVD links no vendor advisory for CVE-2026-120422 yet |
| Reported by The Hacker News | CISA KEV does not list CVE-2026-51990 as exploited in the wild |
| Reported by Infosecurity Magazine | NVD links no vendor advisory for CVE-2026-51990 yet |
Why it matters
This attack shows how attackers can use common apps to compromise users. It highlights the need for stronger security in apps and better protection against DNS hijacking.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is DarkVigil?
DarkVigil is a malware tool that can collect data and stay hidden on a computer. It is used by hackers to spy on users.
How does the attack work?
The hackers trick the Sogou Input Method app to fetch a malicious configuration over the internet. This config tells the app to download and run a backdoor.
Which countries were targeted?
The attack targeted Hong Kong, Thailand, Japan, Vietnam, Sri Lanka, and Oman.
What is SGTool.exe?
SGTool.exe is a component of the Sogou Input Method that fetches and processes configuration data, which can be hijacked by attackers.
How can I protect my device?
Use secure connections like HTTPS, keep software updated, and be cautious with unknown applications.
Related Skillmate posts
Sources
- China-Aligned Hackers Hijack Sogou Input Method DNS Requests to Deploy DarkVigil Backdoor (The Hacker News)
- China-Aligned Group Abuses Sogou Input Method to Deliver Malware (Infosecurity Magazine)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.