Short answer: Gorbag APT group attacked Ukrainian courts and city councils using self-deleting malware. They used spearphishing and RAR files exploiting CVE-2025-8088. To protect, update software and train on phishing awareness.
TL;DR
- Gorbag APT used spearphishing emails with malware.
- They targeted Ukrainian courts and city councils.
- Exploited CVE-2025-8088 in RAR files.
- Malware self-deletes to hide activity.
- Update software and train staff to avoid phishing.
What is CVE-2025-8088?
Gorbag APT is a Russia-aligned group that attacked Ukrainian organizations, including courts and city councils. They used self-deleting malware delivered via spearphishing emails and RAR files exploiting CVE-2025-8088. The malware erased itself after stealing data, making it harder to detect. To prevent attacks, update software and be cautious with emails and files from unknown sources.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Malware
- Harmful software made to spy, steal or damage.
- Exploit
- Code or steps that take advantage of a weakness.
- APT
- An 'advanced persistent threat': a skilled hacking group, often linked to a government, that stays hidden for a long time.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | Help Net Security |
|---|---|
| Date reported | 03 Nov 2026 |
| CVE | CVE-2025-8088 |
| CVSS | 8.4 HIGH CVSS:4.0/AV:L/AC:L/AT:N/PR:N/UI:A/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-35 (see NVD) |
| CISA KEV | Yes, added 2025-08-12; federal due date 2025-09-02 |
| Ransomware use | Known (CISA KEV) |
| Vendor advisory | arstechnica.com |
| Affected product | RARLAB WinRAR |
| Published in NVD | 2025-08-08 (CVE-2025-8088) |
How it works
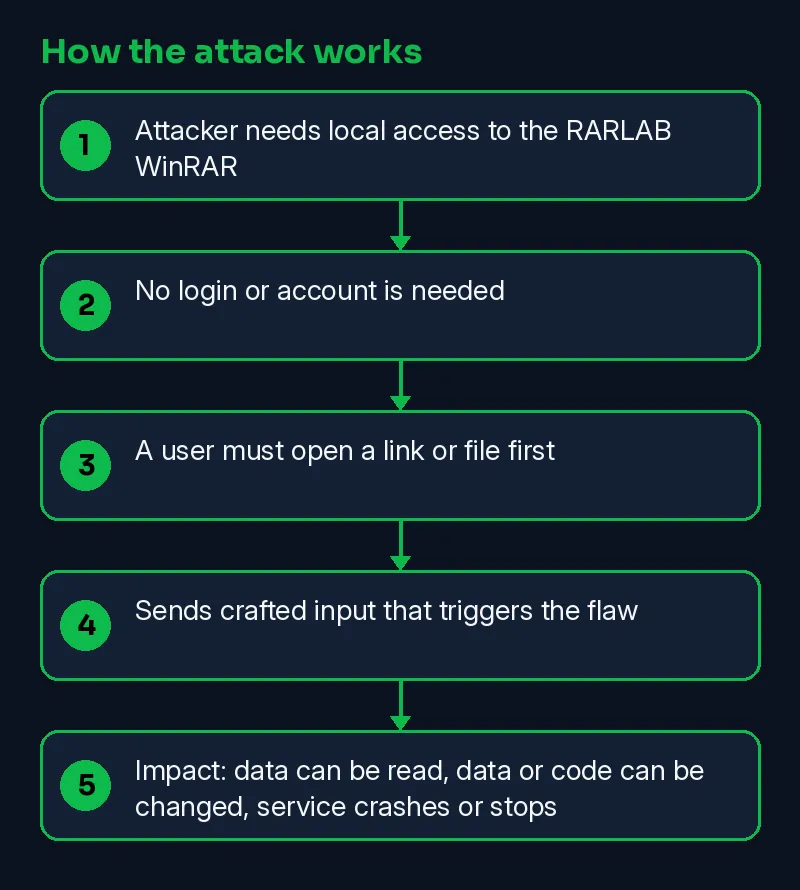
Gorbag APT uses spearphishing emails with Excel files containing hidden malware. In 2025, the malware decodes and runs from %ProgramData%. From early 2026, RAR files exploit CVE-2025-8088, writing LNK files to Startup for persistence. The malware steals credentials and other sensitive data before removing itself.
- Attacker needs local access to the RARLAB WinRAR
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1068 Exploitation for Privilege Escalation
Timeline
| Date | Event | Source |
|---|---|---|
| 2025-08-08 | CVE-2025-8088 published in NVD | NVD |
| 2025-08-12 | CVE-2025-8088 added to CISA KEV (actively exploited) | CISA KEV |
| 2025-09-02 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-03 | Reported by Help Net Security | Help Net Security |
| 2026-11-06 | This Skillmate explainer published | Skillmate |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Microsoft Windows
PowerShell: lists the latest installed updates:
Get-HotFix | Sort-Object InstalledOn -Descending | Select-Object -First 10shows the Windows version and build:
winverHow to fix it
- Update RARLAB WinRAR to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2025-8088 and upgrade to the fixed release it lists.
- CVE-2025-8088 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should watch for odd logins, crashes, and logs of unusual activity.
What is confirmed
- CVE-2025-8088 is a real NVD record scored 8.4 HIGH
- CISA lists CVE-2025-8088 as exploited in the wild
- Reported by Help Net Security
Why it matters
This matters because it shows advanced attackers targeting critical infrastructure. Using self-deleting malware and exploiting known vulnerabilities, they can steal sensitive data without leaving traces, posing a significant threat to security.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is a macro-enabled Excel file?
A macro-enabled Excel file is an Excel document that contains VBA code, which can run automatically or on command. This can be used by attackers to execute harmful code.
How does BeautyStealer work?
BeautyStealer collects sensitive information like browser passwords, cookies, and encryption files. It targets files with extensions like .kdbx, .jks, and .pfx, which store important authentication data.
What is CVE-2025-8088?
CVE-2025-8088 is a path traversal vulnerability in WinRAR that allows attackers to execute arbitrary code. It was used by the Gorbag APT group to infect targets.
Sources
- Gorbag APT group hits Ukrainian courts and city councils with self-deleting malware (Help Net Security)
- Vendor advisory CVE-2025-8088 (arstechnica.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.