Short answer: Russia dismantled the VasyGrek cybercrime group and arrested three suspects. Companies in Russia, Belarus, and Kazakhstan were targeted. Be cautious of phishing emails and use strong passwords.
TL;DR
- Russian authorities arrested three suspects of VasyGrek.
- VasyGrek targeted businesses in Russia, Belarus, and Kazakhstan.
- The group used phishing emails to steal credentials.
- Police seized computers and communications equipment from suspects.
- Victims should be wary of suspicious emails.
What happened?
VasyGrek was a cybercrime group operating in Russia since 2016. They used phishing emails to steal company data and transfer money. Russian police dismantled their operations, arresting three members. They relied on remote access tools and impersonated financial services. Companies in Russia, Belarus, and Kazakhstan were hit. To protect yourself, always verify emails and use strong passwords.
- Phishing
- Fake messages or websites that trick people into giving passwords or money.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | The Record |
|---|---|
| Date reported | 03 Nov 2026 |
How it works
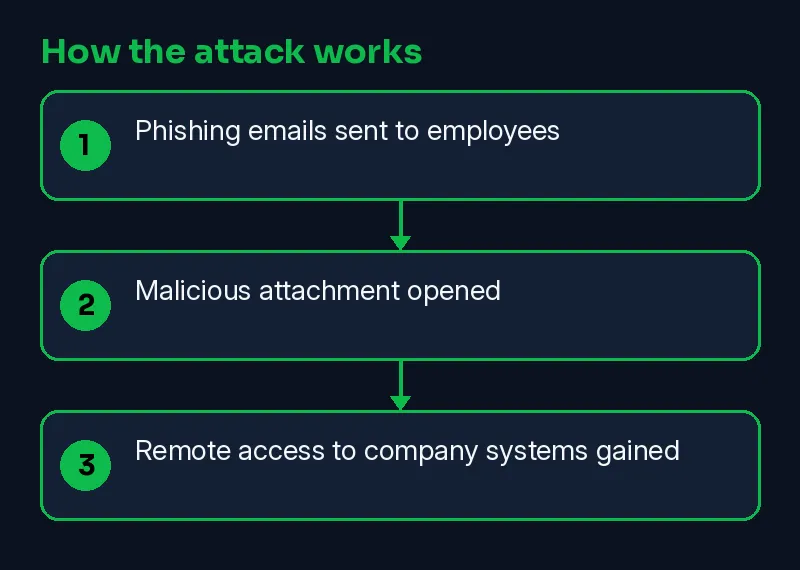
VasyGrek used phishing emails with malicious attachments to steal credentials. They also used remote administration tools to gain access to corporate systems and steal money.
- Phishing emails sent to employees
- Malicious attachment opened
- Remote access to company systems gained
Skillmate analyst mapping (our judgement, not from the vendor):
- T1566 Phishing
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-03 | Reported by The Record | The Record |
| 2026-11-07 | This Skillmate explainer published | Skillmate |
How to fix it
- Keep the operating system, browser and security software updated.
- Do not open unexpected attachments or install software from unofficial sources.
- Report suspicious files or pop-ups to your IT or security team.
How to detect it
Signs of VasyGrek include phishing emails with suspicious attachments or links, odd login attempts, and unauthorized access to corporate systems.
Signs to watch for:
- Unknown programs starting at boot, or new scheduled tasks.
- Security software that was turned off without a reason.
- Unusual outbound connections from a workstation.
What is confirmed
- Reported by The Record
Why it matters
This matters because it shows how cybercriminals use sophisticated phishing and malware tactics to steal money. Companies must improve their security to prevent such attacks.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is VasyGrek?
VasyGrek is a cybercrime group that primarily targets Russian companies with phishing emails and malware. They were active since at least 2016.
What did Russian authorities do about VasyGrek?
Russian authorities arrested three suspected members of VasyGrek and dismantled their infrastructure. The group's leader was placed under house arrest.
How did VasyGrek operate?
VasyGrek used phishing websites and remote administration tools to gain access to victims' computers and steal money.
What were the consequences for the hackers?
The hackers could face up to 10 years in prison for theft and up to 5 years for creating or distributing malicious software.
Sources
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.