
Short answer: APT29 hackers hijacked a web analytics script to deliver exploits for iOS and Android. Websites and visitors are at risk. Keep your devices updated and use strong passwords.
TL;DR
- APT29 hijacked a web analytics script.
- Delivered iOS and Android exploits through compromised websites.
- Vulnerable devices include iPhones and Androids running outdated software.
- Visitors to affected sites risk data theft.
- Keep devices updated and use strong passwords.
What is CVE-2024-27834?
They compromised legitimate websites and used lookalike domains to trick visitors. The attacks can steal cookies, device data, and Wi-Fi passwords. To stay safe, ensure your devices are up to date and use strong passwords.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Exploit
- Code or steps that take advantage of a weakness.
- APT
- An 'advanced persistent threat': a skilled hacking group, often linked to a government, that stays hidden for a long time.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 04 Nov 2026 |
| CVE | CVE-2024-27834 |
| CVSS | 5.5 MEDIUM CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N |
| Weakness | CWE-287 (improper authentication) |
| CISA KEV | Yes, added 2026-11-04; federal due date 2026-11-18 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | support.apple.com |
| CVE | CVE-2024-4671 |
| CVSS | 9.6 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H |
| Weakness | CWE-416 (use after free) |
| CISA KEV | Yes, added 2024-05-13; federal due date 2024-06-03 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | chromereleases.googleblog.com |
| CVE | CVE-2024-5274 |
| CVSS | 9.6 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H |
| Weakness | CWE-843 (see NVD) |
| CISA KEV | Yes, added 2024-05-28; federal due date 2024-06-18 |
| Ransomware use | Unknown (CISA KEV) |
| Affected product | Apple Multiple Products |
| Published in NVD | 2024-05-14 (CVE-2024-27834) |
| Published in NVD | 2024-05-14 (CVE-2024-4671) |
| Published in NVD | 2024-05-28 (CVE-2024-5274) |
How it works
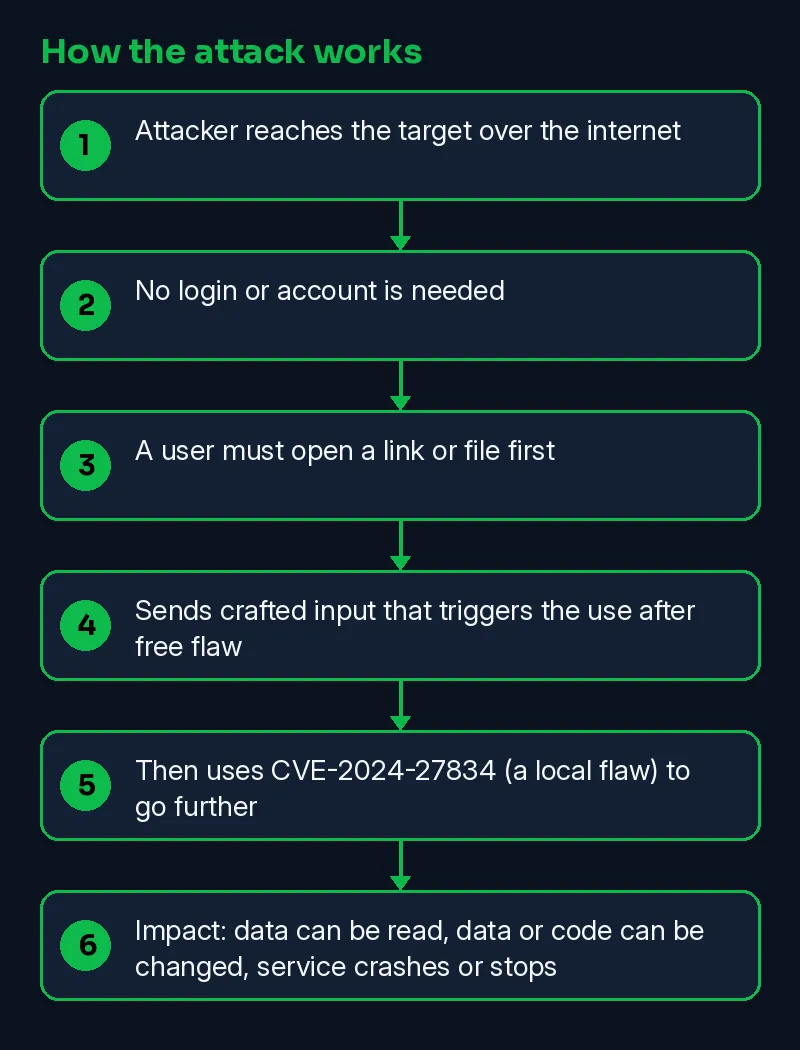
APT29-linked hackers inject malicious JavaScript into legitimate websites and web analytics scripts. They use fake domains and exploit outdated vulnerabilities in iOS and Android devices. The JavaScript collects device information and delivers exploits to steal cookies, Wi-Fi passwords, and device data.
- Attacker reaches the target over the internet
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the use after free flaw
- Then uses CVE-2024-27834 (a local flaw) to go further
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2024-05-13 | CVE-2024-4671 added to CISA KEV (actively exploited) | CISA KEV |
| 2024-05-14 | CVE-2024-27834 published in NVD | NVD |
| 2024-05-14 | CVE-2024-4671 published in NVD | NVD |
| 2024-05-28 | CVE-2024-5274 added to CISA KEV (actively exploited) | CISA KEV |
| 2024-05-28 | CVE-2024-5274 published in NVD | NVD |
| 2024-06-03 | US federal agencies must patch by this date | CISA KEV |
| 2024-06-18 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-04 | CVE-2024-27834 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-04 | Reported by The Hacker News | The Hacker News |
| 2026-11-10 | This Skillmate explainer published | Skillmate |
| 2026-11-18 | US federal agencies must patch by this date | CISA KEV |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Google Chrome
shows the Chrome version:
chrome://settings/help (type in the address bar)How to fix it
- Update Apple Multiple Products to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2024-27834 and upgrade to the fixed release it lists.
- CVE-2024-27834 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2024-4671 and upgrade to the fixed release it lists.
- CVE-2024-4671 is in CISA KEV: treat it as actively exploited and patch first.
- CVE-2024-5274 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders can look for unusual network traffic, failed login attempts, and unexpected crashes.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2024-27834 is a real NVD record scored 5.5 MEDIUM | NVD links no vendor advisory for CVE-2024-5274 yet |
| CISA lists CVE-2024-27834 as exploited in the wild | |
| CVE-2024-4671 is a real NVD record scored 9.6 CRITICAL | |
| CISA lists CVE-2024-4671 as exploited in the wild | |
| CVE-2024-5274 is a real NVD record scored 9.6 CRITICAL | |
| CISA lists CVE-2024-5274 as exploited in the wild | |
| Reported by The Hacker News | |
| Reported by Infosecurity Magazine | |
| Reported by support.apple.com | |
| Reported by chromereleases.googleblog.com |
Why it matters
This matters because APT29 targets high-value websites, risking the data of important visitors. It shows the importance of keeping systems updated and using secure web analytics. Companies and users must stay vigilant to avoid similar attacks.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is APT29?
APT29 is a Russia-linked cyber espionage group also known as Midnight Blizzard or Cozy Bear. They are suspected of launching sophisticated attacks.
How do these attacks spread?
The attackers use compromised websites, fake lookalike domains, and a web analytics service called Plerdy SEO Tracker to spread their malware.
What devices are targeted?
The attacks target both iOS and Android devices, exploiting vulnerabilities in browsers and operating systems.
How can I protect my devices?
Keep your software and devices updated, use strong passwords, and avoid suspicious websites and downloads.
Related Skillmate posts
Sources
- APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits (The Hacker News)
- APT29 Watering Holes Target Unpatched iPhones and Android Devices (Infosecurity Magazine)
- Vendor advisory CVE-2024-27834 (support.apple.com)
- Vendor advisory CVE-2024-4671 (chromereleases.googleblog.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.