
Short answer: Russian hackers used n-day exploits to target iOS and Android devices through compromised websites, stealing data without user interaction. Update your devices to the latest versions to protect yourself.
TL;DR
- Russian hackers targeted iOS and Android users.
- Compromised websites delivered n-day exploits.
- Update your devices to the latest versions.
What is CVE-2024-27834?
This incident involved Russian hackers using n-day exploits to target iOS and Android devices. They compromised legitimate websites and lookalike domains to deliver malicious JavaScript code. This code determined the device and browser version to deploy specific exploits without user interaction, stealing cookies, messaging app databases, and credentials. To stay protected, always keep your devices updated.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Exploit
- Code or steps that take advantage of a weakness.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | BleepingComputer |
|---|---|
| Date reported | 04 Nov 2026 |
| CVE | CVE-2024-27834 |
| CVSS | 5.5 MEDIUM CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N |
| Weakness | CWE-287 (improper authentication) |
| CISA KEV | Yes, added 2026-11-04; federal due date 2026-11-18 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | support.apple.com |
| CVE | CVE-2025-14174 |
| CVSS | 8.8 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H |
| Weakness | CWE-119 (memory buffer error), CWE-787 (out-of-bounds write) |
| CISA KEV | Yes, added 2025-12-12; federal due date 2026-01-02 |
| Ransomware use | Unknown (CISA KEV) |
| CVE | CVE-2025-27038 |
| CVSS | 7.5 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H |
| Weakness | CWE-416 (use after free) |
| CISA KEV | Yes, added 2025-06-03; federal due date 2025-06-24 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | docs.qualcomm.com |
| Affected product | Apple Multiple Products |
| Published in NVD | 2024-05-14 (CVE-2024-27834) |
| Published in NVD | 2025-12-12 (CVE-2025-14174) |
| Published in NVD | 2025-06-03 (CVE-2025-27038) |
How it works
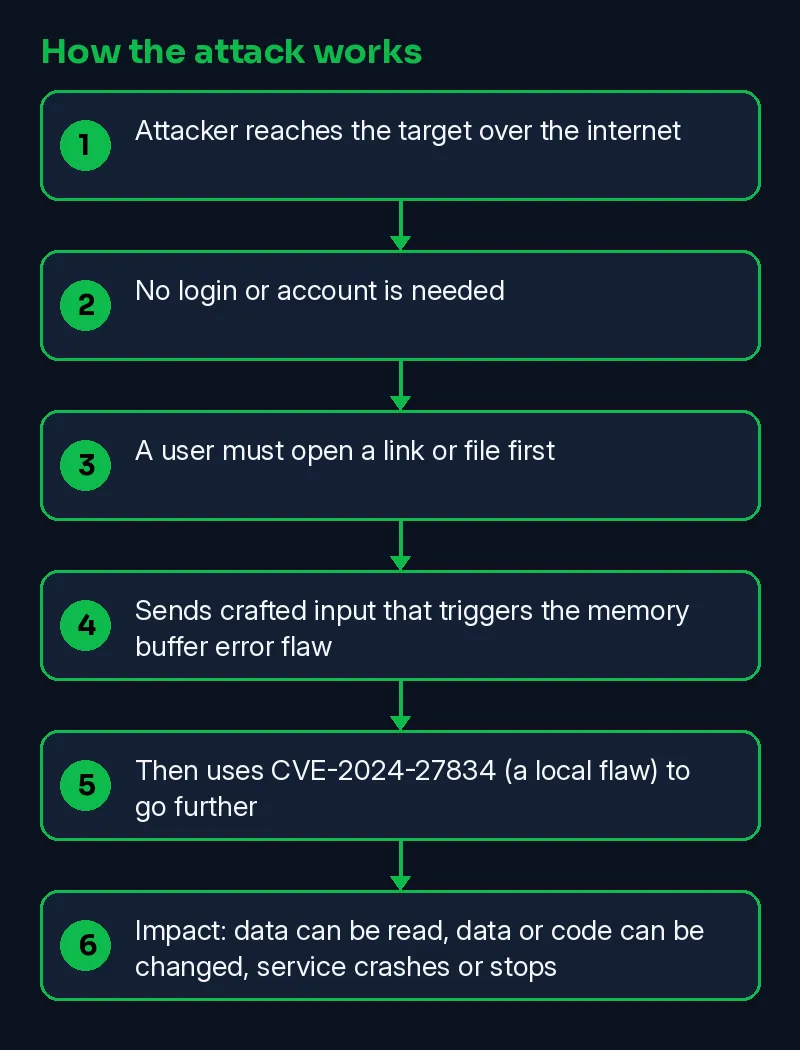
Hackers use compromised websites to deliver JavaScript that profiles visitors. The script determines the browser and device, then sends this info to a C2 server. The server selects the right exploit chain without user interaction, targeting vulnerabilities like cookies and messaging databases.
- Attacker reaches the target over the internet
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the memory buffer error flaw
- Then uses CVE-2024-27834 (a local flaw) to go further
- Impact: data can be read, data or code can be changed, service crashes or stops
Timeline
| Date | Event | Source |
|---|---|---|
| 2024-05-14 | CVE-2024-27834 published in NVD | NVD |
| 2025-06-03 | CVE-2025-27038 added to CISA KEV (actively exploited) | CISA KEV |
| 2025-06-03 | CVE-2025-27038 published in NVD | NVD |
| 2025-06-24 | US federal agencies must patch by this date | CISA KEV |
| 2025-12-12 | CVE-2025-14174 added to CISA KEV (actively exploited) | CISA KEV |
| 2025-12-12 | CVE-2025-14174 published in NVD | NVD |
| 2026-01-02 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-04 | CVE-2024-27834 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-04 | Reported by BleepingComputer | BleepingComputer |
| 2026-11-09 | This Skillmate explainer published | Skillmate |
| 2026-11-18 | US federal agencies must patch by this date | CISA KEV |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Google Chrome
shows the Chrome version:
chrome://settings/help (type in the address bar)How to fix it
- Update Apple Multiple Products to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2024-27834 and upgrade to the fixed release it lists.
- CVE-2024-27834 is in CISA KEV: treat it as actively exploited and patch first.
- CVE-2025-14174 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2025-27038 and upgrade to the fixed release it lists.
- CVE-2025-27038 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders can look for signs like unexpected crashes, odd logins, or JavaScript injection on websites. A false positive might be a legitimate ad or plugin causing similar issues.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2024-27834 is a real NVD record scored 5.5 MEDIUM | NVD links no vendor advisory for CVE-2025-14174 yet |
| CISA lists CVE-2024-27834 as exploited in the wild | |
| CVE-2025-14174 is a real NVD record scored 8.8 HIGH | |
| CISA lists CVE-2025-14174 as exploited in the wild | |
| CVE-2025-27038 is a real NVD record scored 7.5 HIGH | |
| CISA lists CVE-2025-27038 as exploited in the wild | |
| Reported by BleepingComputer | |
| Reported by Help Net Security | |
| Reported by support.apple.com |
Why it matters
This attack matters because it can steal sensitive data from unpatched devices. Companies and users in India and worldwide need to keep their systems updated to prevent such breaches. Students should learn about zero-day exploits and the importance of regular updates.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is a watering hole attack?
A watering hole attack involves compromising a website that the target is likely to visit, to infect the user's device.
What are n-day exploits?
N-day exploits are vulnerabilities that are known but not yet patched, allowing hackers to use them immediately.
What devices were targeted in this attack?
The attack targeted both iOS and Android devices.
How can I protect my device?
Keep your device and software up to date with the latest security patches.
Sources
- Hackers use n-day exploits in zero-click attacks on iOS, Android devices (BleepingComputer)
- Russian hackers target iOS and Android users with n-day exploits (Help Net Security)
- Vendor advisory CVE-2024-27834 (support.apple.com)
- Vendor advisory CVE-2025-27038 (docs.qualcomm.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.