
Short answer: Xen hypervisor had a flaw that allowed a malicious VM to read and write memory of other VMs. Xen users should apply the provided patches.
TL;DR
- Xen 4.6 and later versions are affected.
- The flaw could lead to loss of data privacy.
- Apply the patches provided by Xen Project.
- No known mitigation is available.
What is CVE-2026-102703?
Xen Security Advisory XSA-523 revealed a vulnerability in Xen hypervisor versions 4.6 and later, where a malicious virtual machine (VM) could read and write memory of other VMs. This flaw, discovered by Anthropic and Ada Logics, affects systems running Xen. The Xen Project provided patches to fix the issue, but there are no known workarounds. Users are advised to update their Xen installations.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 04 Nov 2026 |
| CVE | CVE-2026-102703 |
| CVSS | 4.4 MEDIUM CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N |
| Weakness | CWE-704 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | xenbits.xenproject.org |
| CVE | CVE-2026-102704 |
| CVSS | 4.4 MEDIUM CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N |
| Weakness | CWE-693 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | xenbits.xenproject.org |
| Affected product | Xen |
| Published in NVD | 2026-11-04 (CVE-2026-102703) |
| Published in NVD | 2026-11-04 (CVE-2026-102704) |
How it works
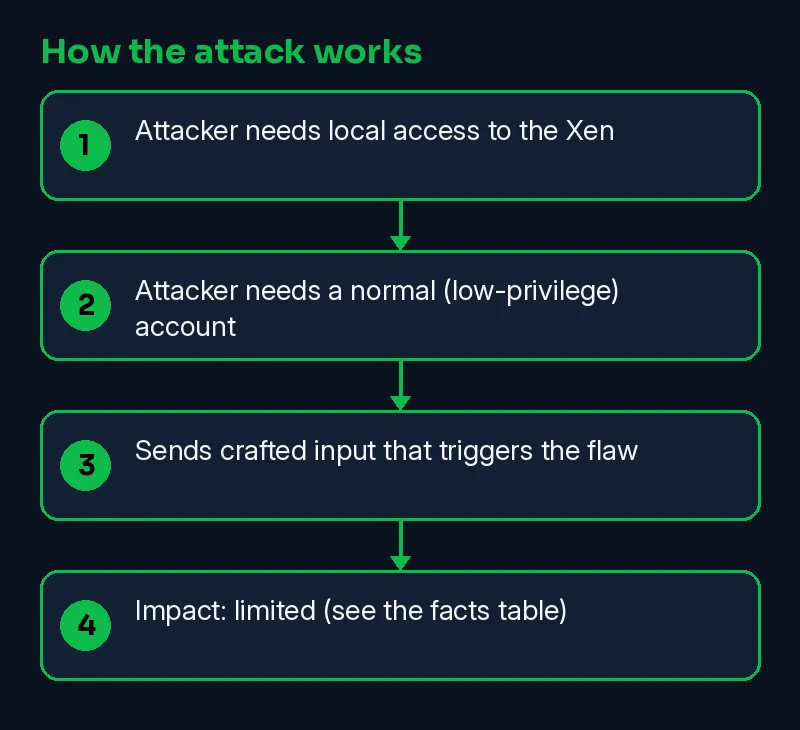
Attackers exploit this by using grant copy operations to read and write other VMs' memory, bypassing security.
- Attacker needs local access to the Xen
- Attacker needs a normal (low-privilege) account
- Sends crafted input that triggers the flaw
- Impact: limited (see the facts table)
Skillmate analyst mapping (our judgement, not from the vendor):
- T1068 Exploitation for Privilege Escalation
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-04 | CVE-2026-102703 published in NVD | NVD |
| 2026-11-04 | CVE-2026-102704 published in NVD | NVD |
| 2026-11-04 | Reported by The Hacker News | The Hacker News |
| 2026-11-09 | This Skillmate explainer published | Skillmate |
How to fix it
- Update Xen to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-102703 and upgrade to the fixed release it lists.
- Read the vendor advisory for CVE-2026-102704 and upgrade to the fixed release it lists.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should look for signs of unexpected memory access patterns or crashes.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-102703 is a real NVD record scored 4.4 MEDIUM | CISA KEV does not list CVE-2026-102703 as exploited in the wild |
| CVE-2026-102704 is a real NVD record scored 4.4 MEDIUM | CISA KEV does not list CVE-2026-102704 as exploited in the wild |
| Reported by The Hacker News | |
| Reported by docs.vates.tech | |
| Reported by security-tracker.debian.org | |
| Reported by xenbits.xenproject.org | |
| Reported by xenbits.xen.org |
Why it matters
This flaw allows a malicious VM to access and modify memory of other VMs, including Dom0. It affects Xen versions from 4.6 onwards, impacting security worldwide.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is CVE-2026-102703?
It's a flaw in Xen that allows a malicious VM to read and write memory of other VMs, including Dom0.
How can I protect my system?
Update your Xen hypervisor to the latest version with the patches provided by the Xen Project Security Team.
Is this issue fixed in Xen 4.5?
No, Xen 4.5 and earlier versions are not vulnerable to this issue.
Can this be exploited by a guest VM in Dom0?
Yes, the flaw allows a guest VM to read and write memory in Dom0, which is a critical vulnerability.
Related Skillmate posts
Sources
- Xen Hypervisor Flaws Let One Malicious VM Read and Write Any Other VM's Memory (The Hacker News)
- Primary source / advisory (docs.vates.tech)
- Primary source / advisory (security-tracker.debian.org)
- Vendor advisory CVE-2026-102703 (xenbits.xenproject.org)
- Xen (primary source) (xenbits.xen.org)
- Xen (primary source) (xenbits.xenproject.org)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.