
Short answer: PTC released patches for a critical flaw in Windchill and FlexPLM that could allow remote code execution. Users should apply the patches immediately. Affected versions include 11.0 M030 and later.
TL;DR
- PTC issued critical patches for Windchill and FlexPLM.
- Affected versions are 11.0 M030 and later.
- Remote code execution is a serious security issue.
- Apply patches as soon as possible.
What is CVE-2026-126325?
PTC identified a critical vulnerability in Windchill and FlexPLM software that could enable remote code execution. This means attackers could run malicious code on the targeted system. The flaw, tracked as CVE-2026-126325, has a high CVSS score of 9.2, indicating it's a significant risk. Patches are available, and users should apply them immediately to protect their systems.
- RCE (remote code execution)
- An attacker can run their own commands on someone else's computer or server over the internet.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- CVSS score
- A 0 to 10 rating of how dangerous a weakness is. 9 or more is critical.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 12 Nov 2026 |
| CVE | CVE-2026-126325 |
| CVSS | 9.2 CRITICAL CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:Y/R:X/V:X/RE:M/U:Amber |
| Weakness | CWE-20 (improper input validation), CWE-502 (unsafe deserialization) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| CVE | CVE-2026-12569 |
| CVSS | 9.3 CRITICAL CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:L/SI:L/SA:L/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:Y/R:U/V:C/RE:X/U:Red |
| Weakness | CWE-20 (improper input validation), CWE-502 (unsafe deserialization) |
| CISA KEV | Yes, added 2026-06-25; federal due date 2026-06-28 |
| Ransomware use | Known (CISA KEV) |
| CVE | CVE-2026-77645 |
| CVSS | 9.2 CRITICAL CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:L/SI:L/SA:L/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:Y/R:U/V:C/RE:M/U:Red |
| Weakness | CWE-20 (improper input validation), CWE-502 (unsafe deserialization) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Affected product | PTC Windchill and FlexPLM |
| Published in NVD | 2026-11-11 (CVE-2026-126325) |
| Published in NVD | 2026-06-18 (CVE-2026-12569) |
| Published in NVD | 2026-08-20 (CVE-2026-77645) |
How it works
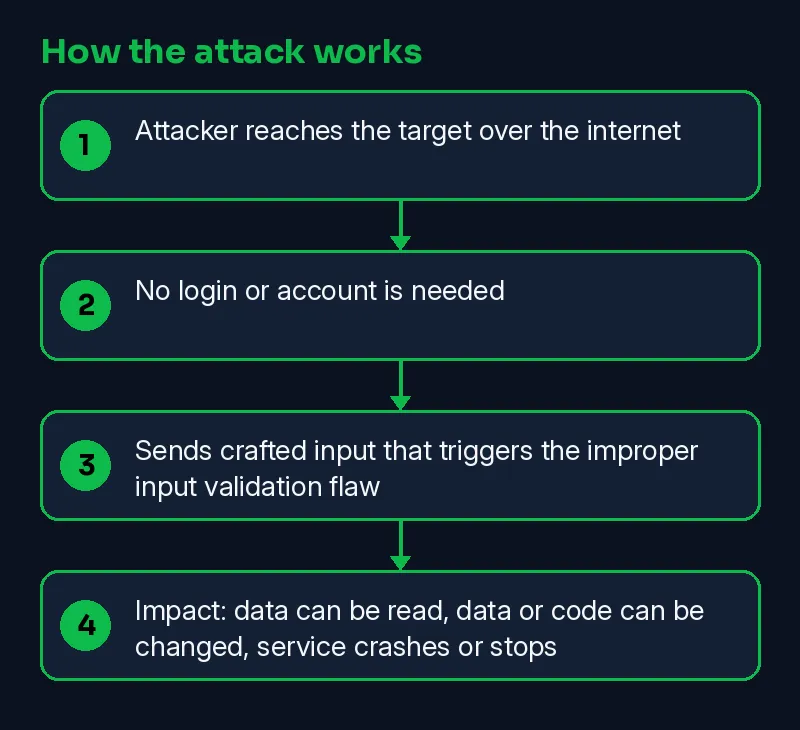
The attack works by sending crafted requests that exploit a vulnerability in how the software handles untrusted data. This can lead to remote code execution, allowing an attacker to run malicious code on the system.
- Attacker reaches the target over the internet
- No login or account is needed
- Sends crafted input that triggers the improper input validation flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-06-18 | CVE-2026-12569 published in NVD | NVD |
| 2026-06-25 | CVE-2026-12569 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-06-28 | US federal agencies must patch by this date | CISA KEV |
| 2026-08-20 | CVE-2026-77645 published in NVD | NVD |
| 2026-11-11 | CVE-2026-126325 published in NVD | NVD |
| 2026-11-12 | Reported by The Hacker News | The Hacker News |
| 2026-11-12 | This Skillmate explainer published | Skillmate |
How to fix it
- Update PTC Windchill and FlexPLM to the fixed release named in the vendor advisory.
- CVE-2026-12569 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should look for signs like unexpected crashes, odd logins, and failed requests.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-126325 is a real NVD record scored 9.2 CRITICAL | CISA KEV does not list CVE-2026-126325 as exploited in the wild |
| CVE-2026-12569 is a real NVD record scored 9.3 CRITICAL | NVD links no vendor advisory for CVE-2026-126325 yet |
| CISA lists CVE-2026-12569 as exploited in the wild | NVD links no vendor advisory for CVE-2026-12569 yet |
| CVE-2026-77645 is a real NVD record scored 9.2 CRITICAL | CISA KEV does not list CVE-2026-77645 as exploited in the wild |
| Reported by The Hacker News | |
| Reported by www.ptc.com |
Why it matters
This matters because it could allow attackers to gain control of systems, steal sensitive data, and disrupt operations. Companies using PTC Windchill and FlexPLM need to apply patches immediately to protect their systems.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What should I do if my PTC Windchill or FlexPLM system is hosted by PTC?
If your system is hosted by PTC, patches have been applied on your behalf, so no action is required from you.
How can I stay updated on the latest patches and security updates?
Subscribing to PTC’s eSupport site and relevant eSupport articles can keep you informed about the latest patches and updates.
What are indicators of compromise (IOCs)?
Indicators of compromise are signs that a system has been compromised, such as specific IP addresses and webshell paths.
Related Skillmate posts
Sources
- PTC Patches Critical Windchill and FlexPLM Flaw That Could Enable Remote Code Execution (The Hacker News)
- Primary source / advisory (www.ptc.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.