
Short answer: Git fixed a flaw that lets attackers run code when you clone a repository recursively. Update Git to the latest version and follow GitHub's advice.
TL;DR
- Git 2.56.1 and backported versions fix the issue.
- Use trusted servers when cloning repositories.
- Do not recursively clone untrusted repositories.
- Do not merge or process untrusted content.
- Update apps that use Git.
What is CVE-2026-105437?
Git is a version control system used for managing code. A recent flaw let attackers run code by setting up a malicious repository. The Git project released updates to fix this issue. Users should update their Git version and follow safety advice to avoid potential attacks.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 11 Nov 2026 |
| CVE | CVE-2026-105437 |
| CVSS | 7.5 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H |
| Weakness | CWE-122 (heap buffer overflow) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| CVE | CVE-2026-111760 (named by the sources; no NVD record yet) |
| CVE | CVE-2026-113408 (named by the sources; no NVD record yet) |
| Affected product | When Git |
| Published in NVD | 2026-11-10 (CVE-2026-105437) |
How it works
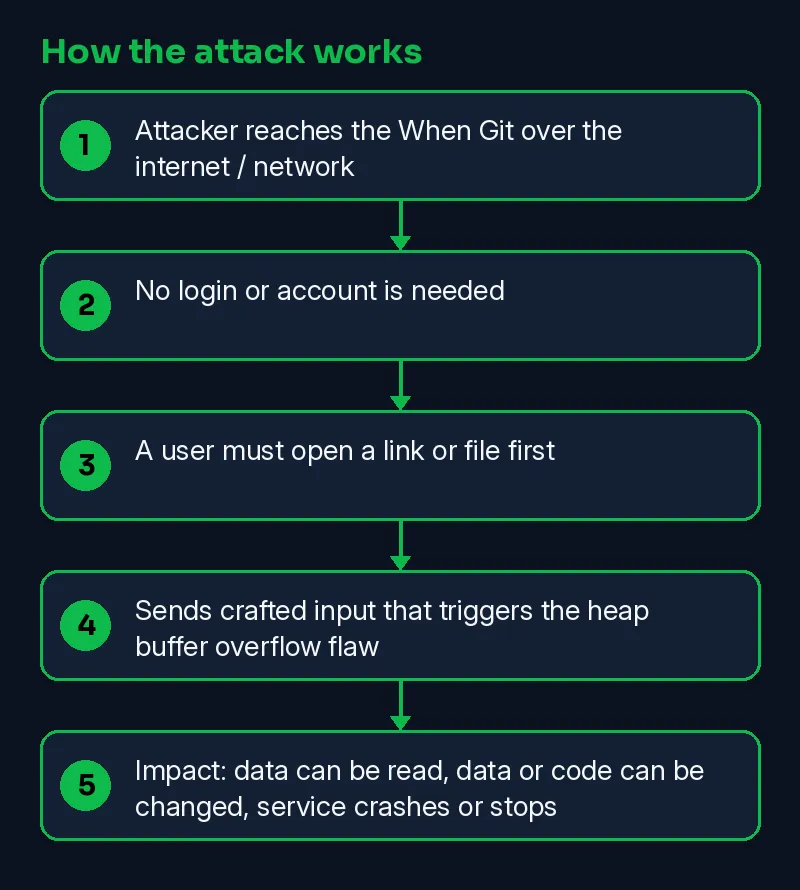
A flaw in Git allows a malicious repository to run attacker code during recursive clones. Extremely long paths are written under a shorter name, enabling attackers to replace .git files with symbolic links to folders containing malicious hooks or configuration. Git runs these folders, executing the attacker's code.
- Attacker reaches the When Git over the internet / network
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the heap buffer overflow flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-10 | CVE-2026-105437 published in NVD | NVD |
| 2026-11-11 | Reported by The Hacker News | The Hacker News |
| 2026-11-11 | This Skillmate explainer published | Skillmate |
How to fix it
- Update When Git to the fixed release named in the vendor advisory.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
A false positive might be a normal merge causing a crash if Git’s version is up to date.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-105437 is a real NVD record scored 7.5 HIGH | CISA KEV does not list CVE-2026-105437 as exploited in the wild |
| Reported by The Hacker News | NVD links no vendor advisory for CVE-2026-105437 yet |
| Reported by github.blog | NVD has no record for CVE-2026-111760 yet |
| NVD has no record for CVE-2026-113408 yet |
Why it matters
This flaw can let malicious code run on computers, compromising systems. Companies and users must update Git to protect against this. Students should be aware of potential vulnerabilities in popular tools like Git.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is Git?
Git is a version control system used to track changes in source code during software development.
How can I protect my system?
Update Git to the latest version, clone only from trusted servers, and avoid merging or processing untrusted content.
What is a merge conflict?
A merge conflict occurs when Git cannot automatically merge changes from different versions of a file.
Related Skillmate posts
Sources
- Git Patches Flaw That Lets Malicious Repositories Execute Code During Recursive Clones (The Hacker News)
- Git (primary source) (github.blog)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.