
Short answer: Citrix fixed 12 security flaws that could cause crashes or let attackers bypass authentication. Users should update their NetScaler and Secure Access Client to the latest versions.
TL;DR
- 12 critical vulnerabilities fixed in NetScaler and Secure Access Client.
- Flaws could lead to denial-of-service or authentication bypass.
- Update to latest versions of NetScaler ADC and Gateway.
What happened?
Citrix identified and patched 12 critical security issues in its NetScaler and Secure Access Client products. These flaws could cause the system to crash or allow attackers to bypass authentication. The vulnerabilities affect NetScaler ADC, Gateway, and Console, as well as Secure Access Client for Windows and Linux. To protect your systems, users should apply the latest updates to their software.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- Authentication bypass
- A trick that lets an attacker get in without a valid password or login.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 12 Nov 2026 |
| CVE | CVE-2026-120868 (named by the sources; no NVD record yet) |
| CVE | CVE-2026-107407 (named by the sources; no NVD record yet) |
| CVE | CVE-2026-107408 (named by the sources; no NVD record yet) |
How it works
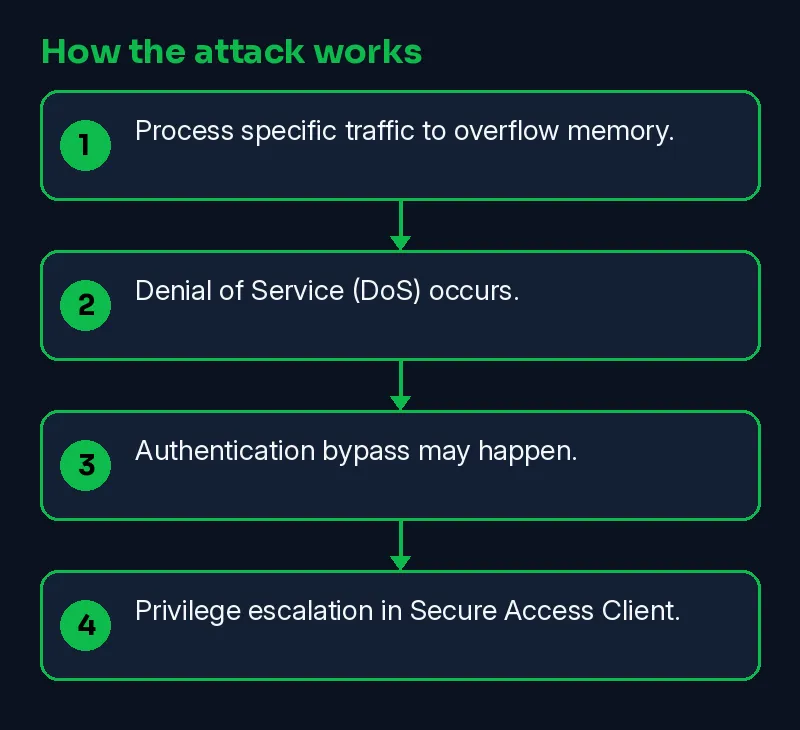
Citrix NetScaler products can have memory overflow issues. When a certain type of traffic is processed, the memory overflows, causing the system to behave unpredictably or crash. This can happen in different parts of the NetScaler, like ADC, Gateway, or Console.
- Process specific traffic to overflow memory.
- Denial of Service (DoS) occurs.
- Authentication bypass may happen.
- Privilege escalation in Secure Access Client.
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-12 | Reported by The Hacker News | The Hacker News |
| 2026-11-13 | This Skillmate explainer published | Skillmate |
How to fix it
- Keep systems and network devices updated and follow vendor security notices.
- Make sure an incident response contact and plan exist before an attack happens.
- Ask your service providers which protections they offer, and test them.
How to detect it
Look for crashes or unexpected behavior in NetScaler and Secure Access Client.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| Reported by The Hacker News | NVD has no record for CVE-2026-120868 yet |
| NVD has no record for CVE-2026-107407 yet | |
| NVD has no record for CVE-2026-107408 yet |
Why it matters
These vulnerabilities can cause NetScaler systems to crash, making services unavailable. They also allow attackers to bypass authentication and escalate privileges, posing significant risks to security and availability. Companies and users should update to secure their systems.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What are the critical vulnerabilities in NetScaler ADC and Gateway?
There are 7 critical memory overflow and corruption vulnerabilities in NetScaler ADC and Gateway that could lead to DoS or authentication bypass.
Are there any flaws in NetScaler Console and Secure Access Client?
Yes, there are 3 flaws: an improper authentication vulnerability in NetScaler Console and privilege escalation vulnerabilities in Secure Access Client for Windows and Linux.
How can I know if I have the latest version of Citrix products?
Check if you are using Citrix NetScaler ADC and Gateway 14.1-73.57 or later, or 13.1-64.39 and later, and NetScaler Console 14.1-74.34 or later.
Related Skillmate posts
Sources
- Citrix Patches 12 NetScaler and Secure Access Client Flaws, Including Authentication Bypass (The Hacker News)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.