
Short answer: Cisco BroadWorks and Openwave flaws are being actively exploited despite available patches. FCEB agencies must apply patches by November 24, 2026, to secure their networks.
TL;DR
- CVE-2026-20320: Unauthenticated attackers can read sensitive config info.
- CVE-2026-111793: Authenticated users can process unintended document types.
- CVE-2026-20127: Unauthenticated attackers can bypass auth and gain admin access.
- Patches are available, but must be applied by FCEB agencies by November 24, 2026.
What is CVE-2026-20320?
These are vulnerabilities in Cisco BroadWorks and Openwave products. Attackers can exploit them to read sensitive data, process unintended files, or gain admin access. CISA has listed these as actively exploited flaws. Cisco provides patches, but users must apply them to prevent attacks.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 11 Nov 2026 |
| CVE | CVE-2026-20320 |
| CVSS | 7.5 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N |
| Weakness | CWE-611 (XML external entity) |
| CISA KEV | Yes, added 2026-11-10; federal due date 2026-11-24 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | sec.cloudapps.cisco.com |
| CVE | CVE-2026-111793 |
| CVSS | 4.3 MEDIUM CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:L |
| Weakness | CWE-669 (see NVD) |
| CISA KEV | Yes, added 2026-11-10; federal due date 2026-11-24 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | github.com |
| CVE | CVE-2026-20127 |
| CVSS | 10.0 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Weakness | CWE-287 (improper authentication) |
| CISA KEV | Yes, added 2026-02-25; federal due date 2026-02-27 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | sec.cloudapps.cisco.com |
| Affected product | Cisco BroadWorks |
| Published in NVD | 2026-08-19 (CVE-2026-20320) |
| Published in NVD | 2026-10-16 (CVE-2026-111793) |
| Published in NVD | 2026-02-25 (CVE-2026-20127) |
How it works
This allows reading sensitive configuration files with the privileges of the Cisco BroadWorks user. Another flaw lets an authenticated user process unintended document types, bypassing the Webmail experience in Openwave Webtop Media Transcoder. A vulnerability in the peering authentication of Cisco Catalyst SD-WAN Controller allows an attacker to bypass authentication and get administrative access, affecting SD-WAN fabric configuration.
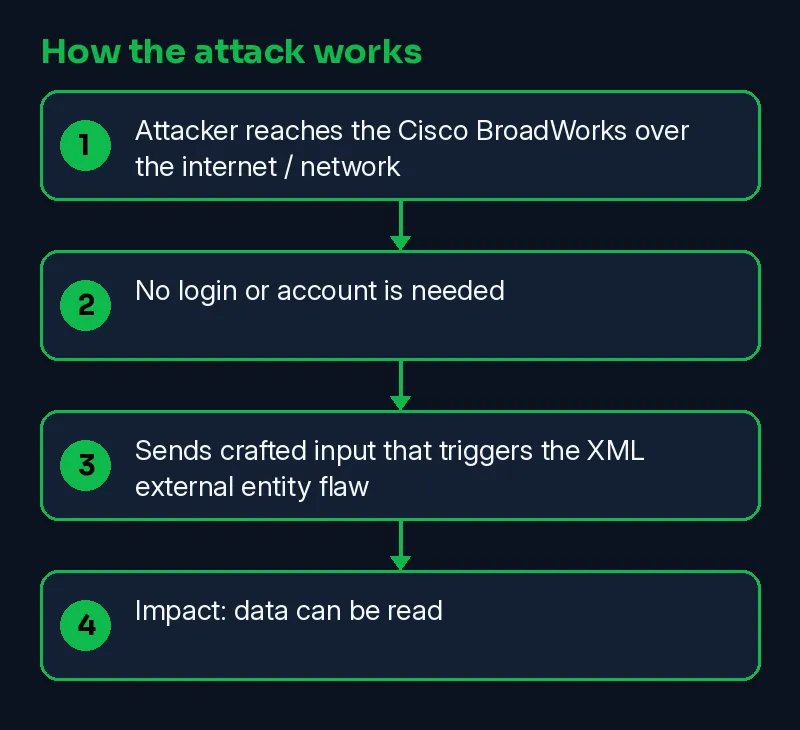
- Attacker reaches the Cisco BroadWorks over the internet / network
- No login or account is needed
- Sends crafted input that triggers the XML external entity flaw
- Impact: data can be read
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-02-25 | CVE-2026-20127 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-02-25 | CVE-2026-20127 published in NVD | NVD |
| 2026-02-27 | US federal agencies must patch by this date | CISA KEV |
| 2026-08-19 | CVE-2026-20320 published in NVD | NVD |
| 2026-10-16 | CVE-2026-111793 published in NVD | NVD |
| 2026-11-10 | CVE-2026-111793 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-10 | CVE-2026-20320 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-11 | Reported by The Hacker News | The Hacker News |
| 2026-11-11 | This Skillmate explainer published | Skillmate |
| 2026-11-24 | US federal agencies must patch by this date | CISA KEV |
How to fix it
- Update Cisco BroadWorks to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-20320 and upgrade to the fixed release it lists.
- CVE-2026-20320 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2026-111793 and upgrade to the fixed release it lists.
- CVE-2026-111793 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2026-20127 and upgrade to the fixed release it lists.
- CVE-2026-20127 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Watch for unauthorized access attempts and unexpected file reads. Logs might show unknown IP addresses trying to log in or sensitive files being accessed.
What is confirmed
- CVE-2026-20320 is a real NVD record scored 7.5 HIGH
- CISA lists CVE-2026-20320 as exploited in the wild
- CVE-2026-111793 is a real NVD record scored 4.3 MEDIUM
- CISA lists CVE-2026-111793 as exploited in the wild
- CVE-2026-20127 is a real NVD record scored 10.0 CRITICAL
- CISA lists CVE-2026-20127 as exploited in the wild
- Reported by The Hacker News
- Reported by github.com
- Reported by sec.cloudapps.cisco.com
Why it matters
These vulnerabilities, despite patches, are actively exploited, posing a significant risk to companies and users. They could lead to data breaches and unauthorized network access. Companies must apply patches and secure their systems to prevent attacks.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What are the CVSS scores for these vulnerabilities?
The CVSS scores are 7.5 for CVE-2026-20320, 4.3 for CVE-2026-111793, and 10.0 for CVE-2026-20127.
How can I protect against these vulnerabilities?
Apply the latest patches and updates. Follow vendor advisories for specific steps to secure your systems.
What are the affected products for CVE-2026-20127?
This vulnerability affects Cisco Catalyst SD-WAN Controller, Cisco Catalyst SD-WAN Manager, and Cisco Catalyst SD-WAN Validator.
Related Skillmate posts
Sources
- Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available Patches (The Hacker News)
- Primary source / advisory (github.com)
- Vendor advisory CVE-2026-20320 (sec.cloudapps.cisco.com)
- Vendor advisory CVE-2026-20127 (sec.cloudapps.cisco.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.