Short answer: SonicWall fixed a flaw that could let attackers bypass security checks. Customers using affected SonicWall devices should update to the latest version. Both tech and non-tech students should stay informed about software updates.
TL;DR
- SonicWall released a patch for a critical vulnerability.
- The flaw affects SonicOS, the operating system for SonicWall firewalls.
- Attackers could bypass SAML authentication and MFA if the flaw is exploited.
- Customers with affected devices should upgrade to the latest version.
What is CVE-2026-19868?
SonicWall has identified a security issue in its SonicOS software that could weaken protection for virtual private networks (VPNs). This vulnerability, tracked as CVE-2026-19868, allows attackers with valid credentials for an alternate authentication method to bypass SAML-based authentication controls. Successful exploitation could also bypass multi-factor authentication. The flaw affects multiple SonicWall device models running SonicOS 7.3.3-7015 or older. To mitigate the risk, SonicWall urges customers to upgrade to the latest release of SonicOS as soon as possible.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Exploit
- Code or steps that take advantage of a weakness.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | SecurityWeek |
|---|---|
| Date reported | 07 Nov 2026 |
| CVE | CVE-2026-19868 |
| CVSS | 7.5 HIGH CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:L/A:N |
| Weakness | CWE-308 (see NVD) |
| CISA KEV | Yes, added 2026-11-06; federal due date 2026-11-20 |
| Ransomware use | Unknown (CISA KEV) |
| CVE | CVE-2026-102255 |
| CVSS | 10.0 CRITICAL CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Weakness | CWE-441 (see NVD), CWE-918 (server-side request forgery) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Affected product | SonicWall SonicOS SSLVPN |
| Published in NVD | 2026-11-06 (CVE-2026-19868) |
| Published in NVD | 2026-10-07 (CVE-2026-102255) |
How it works
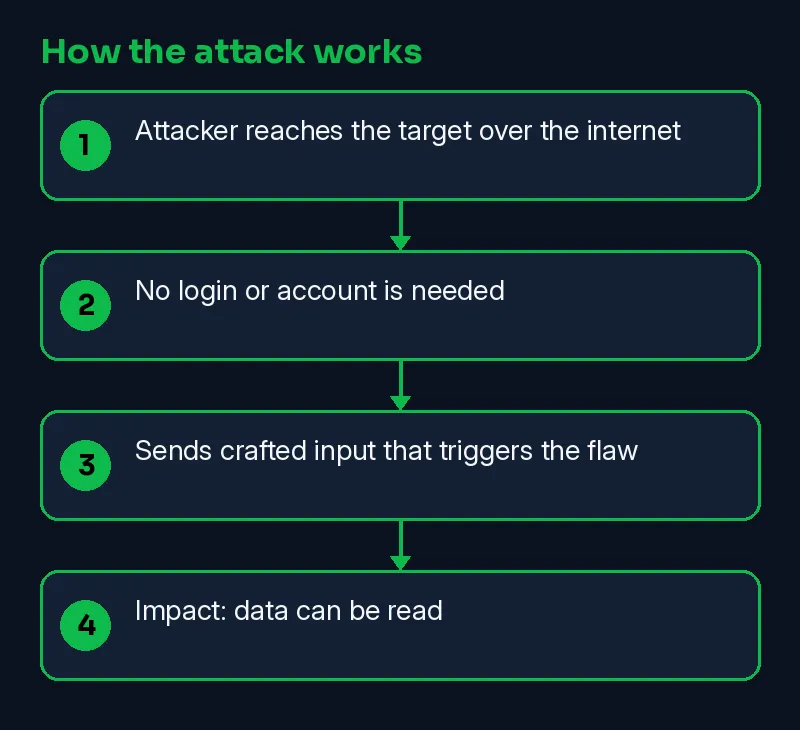
A user with valid login credentials for an alternate method can bypass SAML authentication on SonicOS SSLVPN. This allows them to log in without proper multi-factor authentication. SonicWall patched this in response to a report from Ryan Harris.
- Attacker reaches the target over the internet
- No login or account is needed
- Sends crafted input that triggers the flaw
- Impact: data can be read
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-10-07 | CVE-2026-102255 published in NVD | NVD |
| 2026-11-06 | CVE-2026-19868 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-11-06 | CVE-2026-19868 published in NVD | NVD |
| 2026-11-07 | Reported by SecurityWeek | SecurityWeek |
| 2026-11-07 | This Skillmate explainer published | Skillmate |
| 2026-11-20 | US federal agencies must patch by this date | CISA KEV |
How to fix it
- Update SonicWall SonicOS SSLVPN to the fixed release named in the vendor advisory.
- CVE-2026-19868 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should look for unusual logins or bypassed SAML authentication in logs. However, a user accidentally logging in from a different device might be a false positive.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-19868 is a real NVD record scored 7.5 HIGH | NVD links no vendor advisory for CVE-2026-19868 yet |
| CISA lists CVE-2026-19868 as exploited in the wild | CISA KEV does not list CVE-2026-102255 as exploited in the wild |
| CVE-2026-102255 is a real NVD record scored 10.0 CRITICAL | NVD links no vendor advisory for CVE-2026-102255 yet |
| Reported by SecurityWeek |
Why it matters
This flaw affects SSLVPN devices and could weaken security for remote workers. Companies must update to prevent unauthorized access. Students should learn about vulnerabilities and patches in network security.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
Related Skillmate posts
Sources
- SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins (SecurityWeek)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.