
Short answer: WorkOS, a developer infrastructure company, was breached by an attacker who used ARTEX AI. Business and customer data were accessed, but no production services were affected. Users should stay vigilant for phishing attempts.
TL;DR
- WorkOS suffered a data breach.
- ARTEX AI was used in the attack.
- Customer and business data were accessed.
- Production services were not affected.
- Stay alert for phishing attempts.
What happened at WorkOS?
WorkOS, a company that provides tools for integrating services like authentication and identity management, was breached by an attacker using ARTEX AI. The attacker accessed business contact details, summaries of customer communications, and some customer data. However, the company's main services were not affected. WorkOS advised users to be cautious of phishing attempts.
- Data breach
- When private information is stolen or exposed to people who should not see it.
- Phishing
- Fake messages or websites that trick people into giving passwords or money.
Key facts
| Reported by | BleepingComputer |
|---|---|
| Date reported | 04 Nov 2026 |
How it works
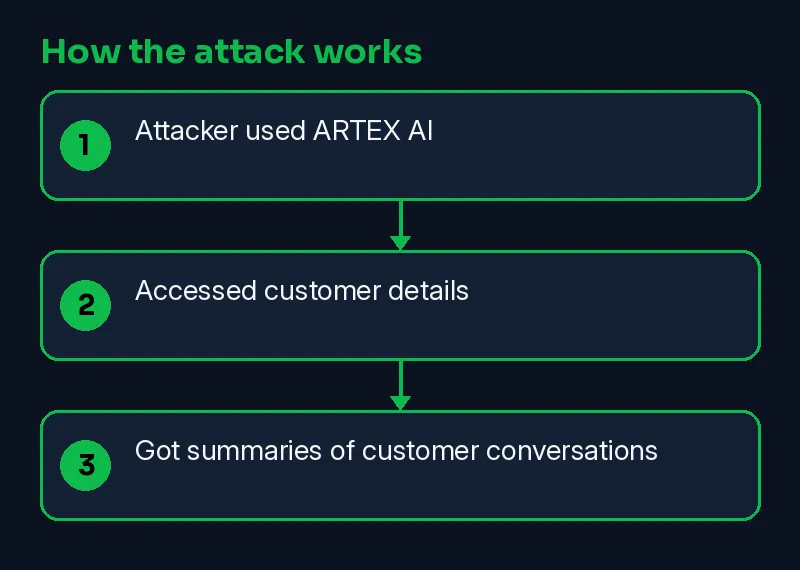
An attacker used a special AI tool called ARTEX to break into a WorkOS app. ARTEX can automatically find and exploit security weaknesses. The attacker got details about customers and their communications, like emails and job titles.
- Attacker used ARTEX AI
- Accessed customer details
- Got summaries of customer conversations
Skillmate analyst mapping (our judgement, not from the vendor):
- T1566 Phishing
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-04 | Reported by BleepingComputer | BleepingComputer |
| 2026-11-08 | This Skillmate explainer published | Skillmate |
How to fix it
- If you have an account with the affected company, change that password and any reused copies of it.
- Turn on two-factor authentication (a second login step) wherever the service offers it.
- Expect phishing emails or calls that use the exposed details; verify requests through official channels.
How to detect it
Signs to watch for:
- Login alerts from new devices or locations on the affected account.
- Password-reset emails you did not ask for.
- Phishing messages that quote your real account details.
What is confirmed
- Reported by BleepingComputer
- Reported by workos.com
Why it matters
This matters because it shows how AI can be used in attacks. Companies need to be vigilant and improve their security measures to protect customer data.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What data was accessed?
The attacker got business contact details, summaries of customer communications, and customer account histories.
How did the attacker get in?
The attacker used an AI-powered offensive security framework called ARTEX AI to automate the attack.
What is ARTEX AI?
ARTEX AI is a penetration testing suite that became private after being used in attacks on banks and other organizations.
What should I do if I suspect a breach?
Disable external access to affected applications and review access controls. Contact a digital forensics firm for help.
Sources
- WorkOS says attacker used ARTEX AI to breach internal sales app (BleepingComputer)
- Primary source / advisory (workos.com)
- WorkOS (primary source) (workos.com)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.