
Short answer: rsync 3.5.2 fixed a flaw that could use weak checksums to exhaust the server's CPU. Update to 3.5.2.
TL;DR
- rsync 3.5.2 fixed a CPU exhaustion issue.
- Update to 3.5.2 to fix the problem.
- Weak checksums can tie up the server's CPU.
What is CVE-2026-119741?
A flaw in version 3.5.1 and earlier versions allowed attackers to send weak checksums that would make the server do lots of work, using up its CPU. The new version 3.5.2 fixes this issue and adds process-priority controls.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
Key facts
| Reported by | Help Net Security |
|---|---|
| Date reported | 04 Nov 2026 |
| CVE | CVE-2026-119741 |
| CVSS | 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-407 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | www.vulncheck.com |
| Affected product | Open-source |
| Fixed versions | 3.5.2 (CVE-2026-119741, per NVD) |
| Published in NVD | 2026-11-03 (CVE-2026-119741) |
How it works
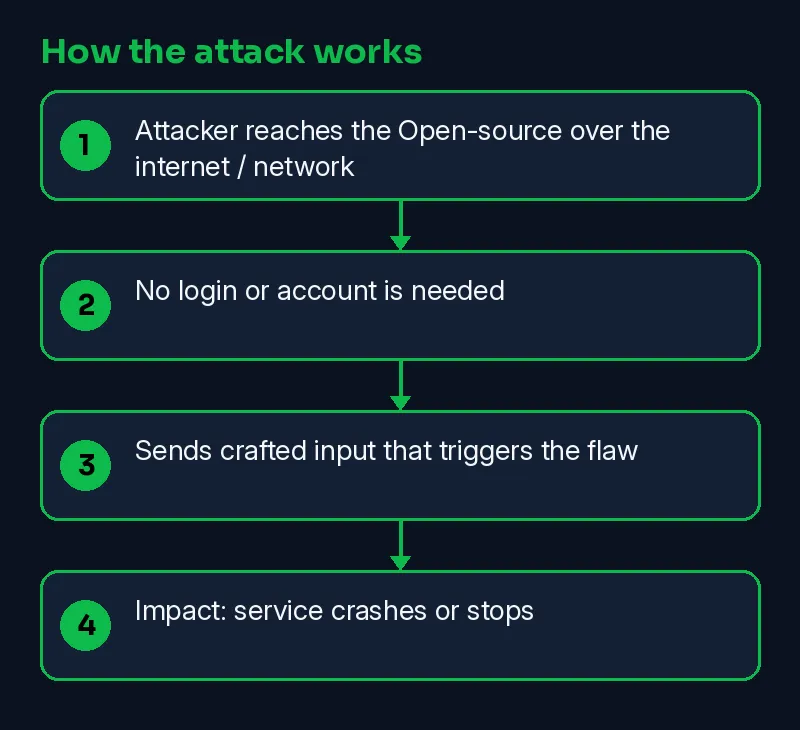
Rsync is a tool that copies files over a network. A flaw in version 3.5.1 and earlier lets a malicious user tie up the server’s CPU by sending weak checksums that cause the server to compute strong checksums that don’t match, using up CPU resources.
- Attacker reaches the Open-source over the internet / network
- No login or account is needed
- Sends crafted input that triggers the flaw
- Impact: service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1499.004 Endpoint Denial of Service: Application or System Exploitation
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-03 | CVE-2026-119741 published in NVD | NVD |
| 2026-11-04 | Reported by Help Net Security | Help Net Security |
| 2026-11-08 | This Skillmate explainer published | Skillmate |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Microsoft Windows
PowerShell: lists the latest installed updates:
Get-HotFix | Sort-Object InstalledOn -Descending | Select-Object -First 10shows the Windows version and build:
winverHow to fix it
- Update Open-source now. NVD lists the fixed versions as 3.5.2.
- Read the vendor advisory for CVE-2026-119741 and upgrade to the fixed release it lists.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should watch for CPU usage spikes, especially when pulling files from a public rsync server.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-119741 is a real NVD record scored 8.7 HIGH | CISA KEV does not list CVE-2026-119741 as exploited in the wild |
| NVD lists fixed versions for CVE-2026-119741: 3.5.2 | |
| Reported by Help Net Security | |
| Reported by www.vulncheck.com |
Why it matters
Updating to version 3.5.2 or later fixes the issue.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What does CVE-2026-119741 mean?
CVE-2026-119741 is a vulnerability in rsync versions before 3.5.2 that allows attackers to use weak checksums to exhaust the server's CPU.
How can I protect against this vulnerability?
Update to rsync 3.5.2, which fixes the CPU exhaustion issue, and use the --nice and --no-nice options to control the priority of the local and remote processes.
Is this vulnerability serious?
Yes, it is rated CVSS 8.7, which is considered high. It can cause the server's CPU to be exhausted, affecting its performance.
Sources
- Open-source file sync tool rsync 3.5.2 fixes a CPU exhaustion flaw (Help Net Security)
- Vendor advisory CVE-2026-119741 (www.vulncheck.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.