
Short answer: Goddess of Victory: NIKKE’s PC launcher was hacked, spreading malware. Players and their data may be at risk. Update your game and monitor your accounts.
TL;DR
- Hackers tampered with the launcher's script files.
- Malware steals credentials and cryptocurrency wallet data.
- Level Infinite issued an update on Nov 4, 2026.
- Check for signs of compromise and update your game.
What happened?
A supply-chain attack where hackers modified the PC launcher scripts of the game Goddess of Victory: NIKKE. This allowed malware to be installed on players' computers, stealing sensitive information. The attack targeted both players and their cryptocurrency wallets. Level Infinite quickly issued a fix, but some malicious scripts may still be active. Players should update their game and be cautious of any unusual activity.
- Malware
- Harmful software made to spy, steal or damage.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | BleepingComputer |
|---|---|
| Date reported | 04 Nov 2026 |
How it works
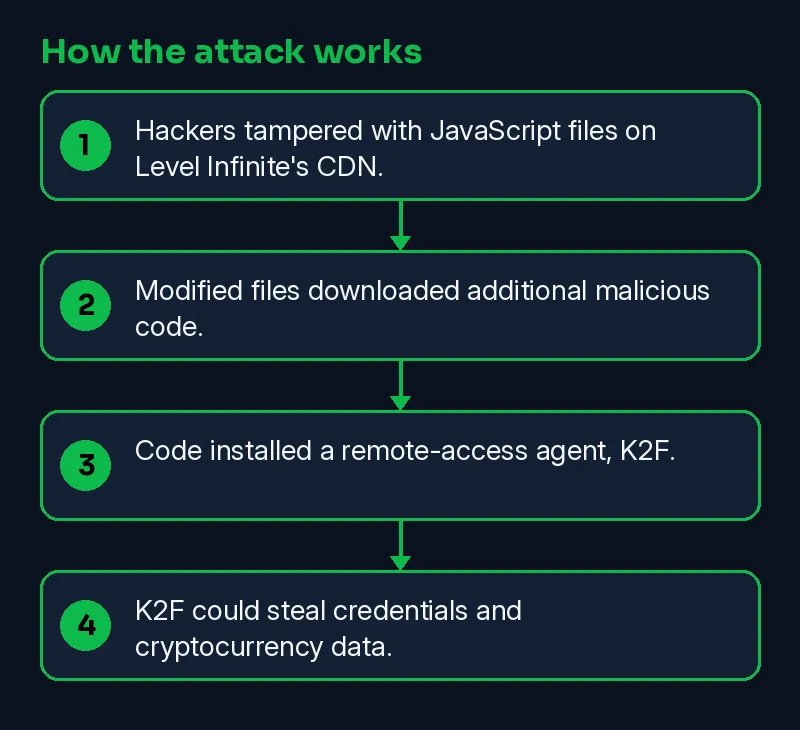
Hackers modified the game launcher scripts, injecting malicious code that downloaded additional malware. The malware, called K2F, allowed attackers to steal credentials and cryptocurrency data.
- Hackers tampered with JavaScript files on Level Infinite's CDN.
- Modified files downloaded additional malicious code.
- Code installed a remote-access agent, K2F.
- K2F could steal credentials and cryptocurrency data.
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-04 | Reported by BleepingComputer | BleepingComputer |
| 2026-11-11 | This Skillmate explainer published | Skillmate |
How to fix it
- Keep the operating system, browser and security software updated.
- Do not open unexpected attachments or install software from unofficial sources.
- Report suspicious files or pop-ups to your IT or security team.
How to detect it
Defenders should check logs for unusual activity, crashes, or odd login attempts.
Signs to watch for:
- Unknown programs starting at boot, or new scheduled tasks.
- Security software that was turned off without a reason.
- Unusual outbound connections from a workstation.
What is confirmed
- Reported by BleepingComputer
- Reported by nikke-en.com
Why it matters
This attack highlights supply-chain risks. Companies must secure third-party services and monitor for tampering. Users should update promptly and check for security warnings.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is a supply-chain attack?
A supply-chain attack happens when hackers target software or services used by a company, not the company itself. In this case, the game launcher was tampered with.
How did the hackers spread the malware?
They modified JavaScript files hosted on Level Infinite’s CDN, injecting malicious code that downloaded additional malware when players opened the game launcher.
What kind of data could be stolen?
The malware could steal credentials, cryptocurrency wallet data, and information from web browsers. It could also capture screenshots and browse local files.
How can I check if my system was affected?
Look for the string 'k2f_chan' in the NIKKE installation directory’s debug.log file. This could indicate the malware executed.
Sources
- NIKKE PC game launcher hacked to spread remote access, data-stealing malware (BleepingComputer)
- NIKKE (primary source) (nikke-en.com)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.