
Short answer: N-able released hotfixes for zero-day vulnerabilities in its N-central RMM platform. IT departments and MSPs are affected. Update to the latest version as soon as possible.
TL;DR
- N-able released security patches for N-central.
- Zero-day vulnerabilities were disclosed by a security researcher.
- N-central versions before 26.4.1 are affected.
- IT departments and MSPs should upgrade immediately.
What is CVE-2026-125878?
N-able N-central is a remote monitoring and management platform used by IT departments and managed service providers. Recently, it faced zero-day vulnerabilities that could allow attackers to perform actions like remote code execution, privilege escalation, and cross-site scripting. These vulnerabilities were discovered by a security researcher and disclosed publicly. N-able released security hotfixes to address these issues. Users of N-central should ensure they are running the latest version to protect their systems.
- RCE (remote code execution)
- An attacker can run their own commands on someone else's computer or server over the internet.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Zero-day
- A weakness attackers use before the maker has released a fix.
Key facts
| Reported by | BleepingComputer |
|---|---|
| Date reported | 11 Nov 2026 |
| CVE | CVE-2026-125878 |
| CVSS | 8.7 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:H/VA:L/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-79 (cross-site scripting) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | me.n-able.com |
| CVE | CVE-2026-125879 |
| CVSS | 8.6 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:N/VC:H/VI:H/VA:L/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-266 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | me.n-able.com |
| CVE | CVE-2026-125880 |
| CVSS | 8.3 HIGH CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:A/VC:H/VI:H/VA:L/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-644 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| Vendor advisory | me.n-able.com |
| Affected product | N-able |
| Fixed versions | 26.4.1. (CVE-2026-125878, per NVD) |
| Fixed versions | 26.4.1. (CVE-2026-125879, per NVD) |
| Fixed versions | 26.4.1. (CVE-2026-125880, per NVD) |
| Published in NVD | 2026-11-10 (CVE-2026-125878) |
| Published in NVD | 2026-11-10 (CVE-2026-125879) |
| Published in NVD | 2026-11-10 (CVE-2026-125880) |
How it works
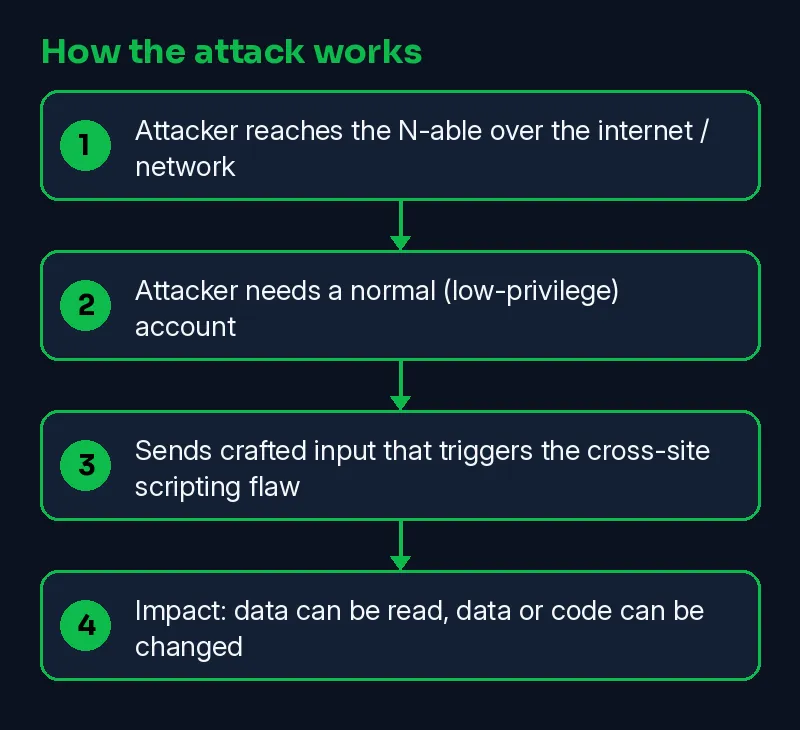
N-able's N-central software has security issues. Attackers can send malicious input that tricks the system. For example, they can inject code that runs on the server, or change settings to gain more control over the system.
- Attacker reaches the N-able over the internet / network
- Attacker needs a normal (low-privilege) account
- Sends crafted input that triggers the cross-site scripting flaw
- Impact: data can be read, data or code can be changed
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-10 | CVE-2026-125878 published in NVD | NVD |
| 2026-11-10 | CVE-2026-125879 published in NVD | NVD |
| 2026-11-10 | CVE-2026-125880 published in NVD | NVD |
| 2026-11-11 | Reported by BleepingComputer | BleepingComputer |
| 2026-11-11 | This Skillmate explainer published | Skillmate |
How to fix it
- Update N-able now. NVD lists the fixed versions as 26.4.1.; 26.4.1.; 26.4.1..
- Read the vendor advisory for CVE-2026-125878 and upgrade to the fixed release it lists.
- Read the vendor advisory for CVE-2026-125879 and upgrade to the fixed release it lists.
- Read the vendor advisory for CVE-2026-125880 and upgrade to the fixed release it lists.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-125878 is a real NVD record scored 8.7 HIGH | CISA KEV does not list CVE-2026-125878 as exploited in the wild |
| CVE-2026-125879 is a real NVD record scored 8.6 HIGH | CISA KEV does not list CVE-2026-125879 as exploited in the wild |
| CVE-2026-125880 is a real NVD record scored 8.3 HIGH | CISA KEV does not list CVE-2026-125880 as exploited in the wild |
| NVD lists fixed versions for CVE-2026-125878: 26.4.1. | |
| NVD lists fixed versions for CVE-2026-125879: 26.4.1. | |
| NVD lists fixed versions for CVE-2026-125880: 26.4.1. | |
| Reported by BleepingComputer |
Why it matters
These vulnerabilities can let attackers take full control of N-central servers, steal data, and disrupt services. Companies and users must update to protect their systems and sensitive information.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What are the main risks of these vulnerabilities?
These vulnerabilities can allow attackers to execute code, steal data, and gain administrative access.
How can I protect my system from these vulnerabilities?
Keep your system updated to the latest version and follow N-able's upgrade guidance.
What should I do if I suspect my system is affected?
Immediately upgrade to the latest version and check for any unauthorized access or changes.
Are these vulnerabilities still active?
While N-able hasn't confirmed active exploitation, threat intelligence suggests attackers are scanning for them.
Sources
- N-able releases security hotfixes for zero-day vulnerabilities (BleepingComputer)
- Vendor advisory CVE-2026-125878 (me.n-able.com)
- Vendor advisory CVE-2026-125879 (me.n-able.com)
- Vendor advisory CVE-2026-125880 (me.n-able.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.