Short answer: October 2026 Patch Tuesday saw 1,407 unique CVEs fixed, with one zero-day exploited. Organizations using old software are at risk. Keep systems updated and remove obsolete software.
TL;DR
- 1,407 critical vulnerabilities fixed.
- One zero-day exploited in Windows.
- PHP2Shell vulnerabilities exploited in the wild.
- Seven certificates removed from Windows trust list.
- Remove unused software to avoid risks.
What is CVE-2026-96951?
Microsoft released 1,407 security fixes in October 2026, including a record-breaking number of critical vulnerabilities. One zero-day exploit, CVE-2026-96951, allowed attackers to bypass security features in Windows 10, 11, and Server. Another, CVE-2026-10839, let attackers redirect users to malicious sites. Microsoft also fixed several certificates and issues with their Always On VPN and Smart App Control. Obsolete software, like an old 2014 application still running on 2.5 million devices, can pose risks. Updates are crucial to protect against these vulnerabilities.
- RCE (remote code execution)
- An attacker can run their own commands on someone else's computer or server over the internet.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- Zero-day
- A weakness attackers use before the maker has released a fix.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Exploit
- Code or steps that take advantage of a weakness.
Key facts
| Reported by | Help Net Security |
|---|---|
| Date reported | 06 Nov 2026 |
| CVE | CVE-2026-96951 |
| CVSS | 8.8 HIGH CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H |
| Weakness | CWE-77 (see NVD) |
| CISA KEV | Yes, added 2026-10-13; federal due date 2026-10-16 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | msrc.microsoft.com |
| CVE | CVE-2026-10839 |
| CVSS | 5.1 MEDIUM CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:A/VC:L/VI:L/VA:N/SC:L/SI:L/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-601 (see NVD) |
| CISA KEV | Not listed (no confirmed exploitation in KEV) |
| CVE | CVE-2026-109618 |
| CVSS | 9.2 CRITICAL CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X |
| Weakness | CWE-1325 (see NVD), CWE-416 (use after free), CWE-755 (see NVD) |
| CISA KEV | Yes, added 2026-10-26; federal due date 2026-10-29 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | github.com |
| Affected product | Microsoft Windows |
| Published in NVD | 2026-10-13 (CVE-2026-96951) |
| Published in NVD | 2026-06-17 (CVE-2026-10839) |
| Published in NVD | 2026-10-21 (CVE-2026-109618) |
How it works
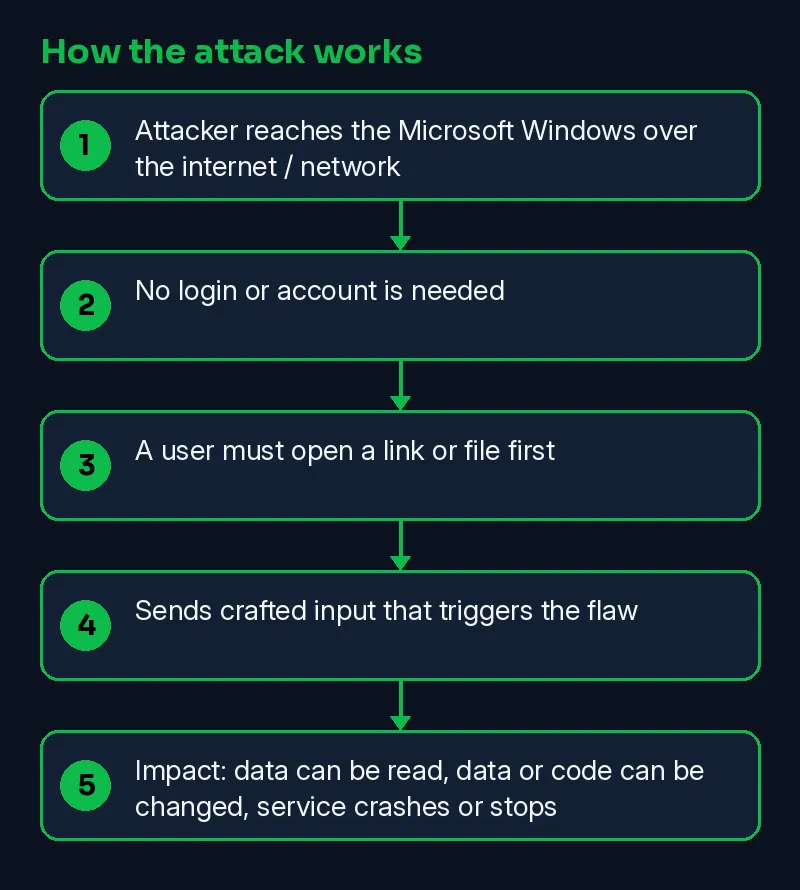
In CVE-2026-96951, attackers can send specially crafted commands through a network to bypass security features in Windows. This happens when special elements are not properly neutralized in commands. In CVE-2026-10839, attackers use manipulated values in the X-Forwarded-Host header to redirect users to malicious sites. This is an open redirection vulnerability in the authentication system. In CVE-2026-109618, attackers exploit out-of-memory (OOM) conditions in PHP. When request memory is uninitialized, the cleanup procedure can read or branch on this memory, leading to remote code execution (RCE).
- Attacker reaches the Microsoft Windows over the internet / network
- No login or account is needed
- A user must open a link or file first
- Sends crafted input that triggers the flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Skillmate analyst mapping (our judgement, not from the vendor):
- T1190 Exploit Public-Facing Application
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-06-17 | CVE-2026-10839 published in NVD | NVD |
| 2026-10-13 | CVE-2026-96951 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-10-13 | CVE-2026-96951 published in NVD | NVD |
| 2026-10-16 | US federal agencies must patch by this date | CISA KEV |
| 2026-10-21 | CVE-2026-109618 published in NVD | NVD |
| 2026-10-26 | CVE-2026-109618 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-10-29 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-06 | Reported by Help Net Security | Help Net Security |
| 2026-11-07 | This Skillmate explainer published | Skillmate |
Am I affected?
These commands only read the version or settings. Compare the output with the vendor advisory linked in the facts table.
Microsoft Windows
PowerShell: lists the latest installed updates:
Get-HotFix | Sort-Object InstalledOn -Descending | Select-Object -First 10shows the Windows version and build:
winverHow to fix it
- Update Microsoft Windows to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-96951 and upgrade to the fixed release it lists.
- CVE-2026-96951 is in CISA KEV: treat it as actively exploited and patch first.
- Read the vendor advisory for CVE-2026-109618 and upgrade to the fixed release it lists.
- CVE-2026-109618 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Check your system logs for any unusual activity, crashes, or odd login attempts. Ensure all software, especially older versions, is up to date. Verify the version numbers of critical software like PHP and Windows. Look for any unexpected network connections or requests that could indicate a vulnerability. Regularly check for certificate revocation lists to ensure your trust settings are correct.
What is confirmed and what is not
| Confirmed | Not confirmed yet |
|---|---|
| CVE-2026-96951 is a real NVD record scored 8.8 HIGH | CISA KEV does not list CVE-2026-10839 as exploited in the wild |
| CISA lists CVE-2026-96951 as exploited in the wild | NVD links no vendor advisory for CVE-2026-10839 yet |
| CVE-2026-10839 is a real NVD record scored 5.1 MEDIUM | |
| CVE-2026-109618 is a real NVD record scored 9.2 CRITICAL | |
| CISA lists CVE-2026-109618 as exploited in the wild | |
| Reported by Help Net Security | |
| Reported by github.com |
Why it matters
Old software is a big risk. In November 2026, Microsoft fixed 1,407 bugs, but only 78 were critical. These can give attackers full control. Not removing old software can also expose systems. In one case, a 2014 app was still running on 2.5 million Windows devices, risking millions of machines.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is CVE-2026-96951?
CVE-2026-96951 is a security issue in Windows Shell. It allows attackers to bypass security features over the network.
How many vulnerabilities were patched in October 2026 Patch Tuesday?
Microsoft patched 1,407 unique vulnerabilities in October 2026 Patch Tuesday.
What is the main vulnerability in PHP mentioned in the sources?
The main PHP vulnerability mentioned is CVE-2026-109618, which allows remote code execution through out-of-memory (OOM) errors.
Related Skillmate posts
Sources
- November 2026 Patch Tuesday forecast: Old software continues to bite (Help Net Security)
- Vendor advisory CVE-2026-109618 (github.com)
- Vendor advisory CVE-2026-96951 (msrc.microsoft.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.
Watch today's video brief: https://youtu.be/kRYzVvFUDME