Short answer: Government servers were targeted with SysGoRAT and AI-generated scripts. Users should keep systems updated and use strong passwords.
TL;DR
- Attackers targeted government Linux servers.
- Used SysGoRAT and AI-generated scripts.
- Attempted to steal sensitive data and emails.
What happened?
This incident involves cyber attackers targeting government Linux servers. They used a tool called SysGoRAT and AI-generated scripts to steal sensitive information and emails. To protect yourself, keep your systems updated and use strong passwords.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 02 Nov 2026 |
How it works
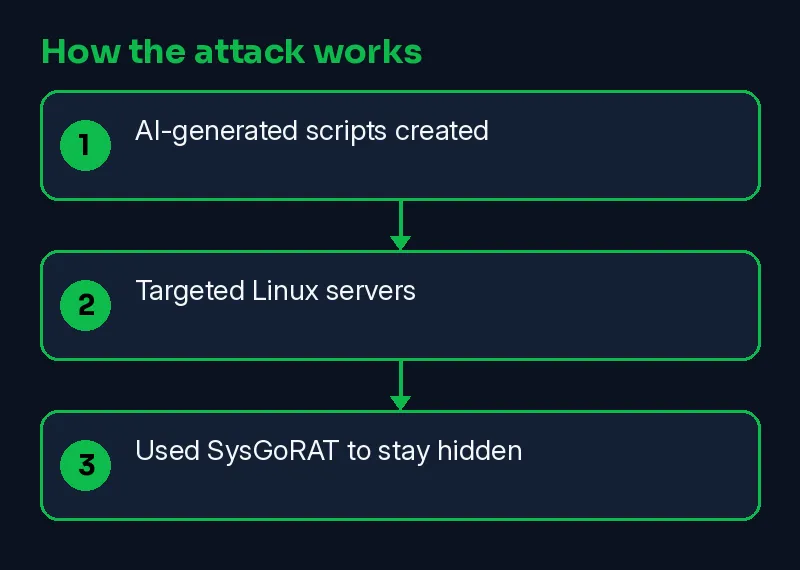
Hackers used AI to create malicious scripts. They targeted Linux servers, especially those of governments. They also created a script to compress emails into ZIP files.
- AI-generated scripts created
- Targeted Linux servers
- Used SysGoRAT to stay hidden
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-02 | Reported by The Hacker News | The Hacker News |
| 2026-11-03 | This Skillmate explainer published | Skillmate |
How to fix it
- Keep the operating system, browser and security software updated.
- Do not open unexpected attachments or install software from unofficial sources.
- Report suspicious files or pop-ups to your IT or security team.
How to detect it
Defenders should watch for unusual logins, unexpected crashes, and changes in system files.
Signs to watch for:
- Unknown programs starting at boot, or new scheduled tasks.
- Security software that was turned off without a reason.
- Unusual outbound connections from a workstation.
What is confirmed
- Reported by The Hacker News
Why it matters
This attack shows the growing use of AI in cyberattacks. It highlights the need for better defenses against AI-generated threats. Companies and users must stay vigilant to protect sensitive data.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is SysGoRAT?
SysGoRAT is a custom, multi-platform remote access trojan written in Go. It supports various persistence methods and can operate on both Windows and Linux systems.
How do attackers maintain persistence in the system?
Attackers use custom cross-platform backdoors, web shells, and scripts to maintain persistence. They replace .bashrc files, inject code into PHP login pages, and use command history to steal credentials.
What are the main goals of the attackers?
The attackers aim to gather sensitive information, exfiltrate data, and access social media accounts. They specifically target government Linux servers and state-affiliated infrastructure.
Sources
- Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts (The Hacker News)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.