
Short answer: ScreenConnect users face risks from SCKit malware. Patch your software and disable third-party extensions. Check your accounts for unusual activity.
TL;DR
- ScreenConnect has a flaw that lets attackers use support sessions.
- SCKit malware can hijack sessions and deploy malicious code.
- Disable third-party extensions in ScreenConnect to secure your environment.
- Monitor your accounts for unusual activity and suspicious connections.
What is CVE-2026-84869?
A security issue called SCKit malware targets ScreenConnect. It uses flaws like CVE-2026-84869 to hijack support sessions and deploy malware. To protect yourself, ensure you have the latest patches and disable any unnecessary third-party extensions. Regularly check for any unusual activities in your accounts and systems.
- Vulnerability
- A mistake or weakness in software that an attacker can misuse.
- Patch
- A software update from the maker that fixes a security weakness.
- CVE
- A public ID number (like CVE-2026-12345) given to a known security weakness so everyone can talk about the same bug.
- Malware
- Harmful software made to spy, steal or damage.
Key facts
| Reported by | The Hacker News |
|---|---|
| Date reported | 12 Nov 2026 |
| CVE | CVE-2026-84869 |
| CVSS | 9.9 CRITICAL CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H |
| Weakness | CWE-269 (improper privilege management), CWE-862 (missing authorization) |
| CISA KEV | Yes, added 2026-09-11; federal due date 2026-09-14 |
| Ransomware use | Unknown (CISA KEV) |
| Vendor advisory | www.connectwise.com |
| Affected product | ConnectWise ScreenConnect |
| Published in NVD | 2026-09-08 (CVE-2026-84869) |
How it works
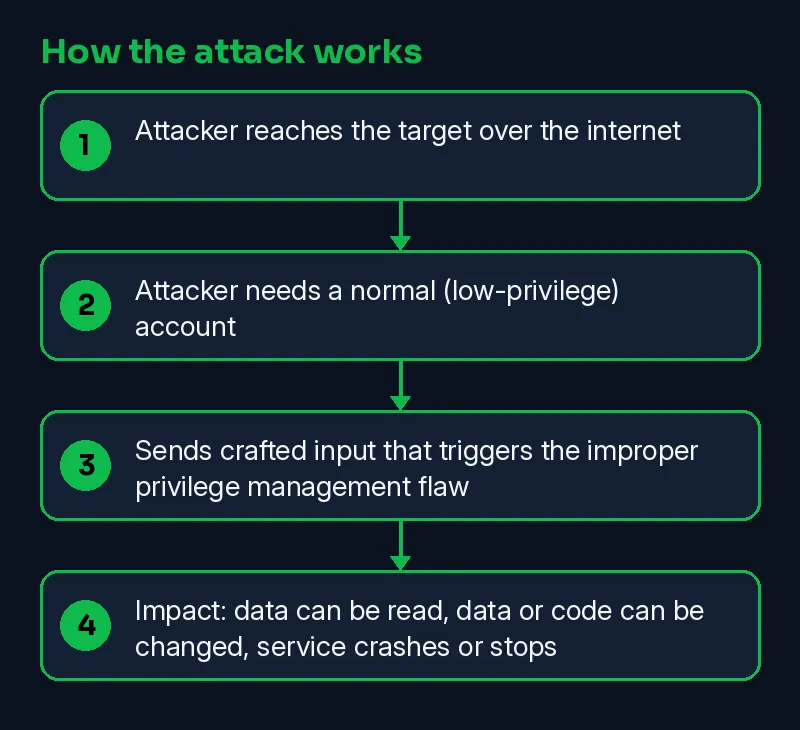
First, an attacker uses a critical flaw in ScreenConnect to gain control. They then download a tool called SCKit, which hijacks sessions and installs malware. Finally, the malware uses ScreenConnect features to spread to other machines.
- Attacker reaches the target over the internet
- Attacker needs a normal (low-privilege) account
- Sends crafted input that triggers the improper privilege management flaw
- Impact: data can be read, data or code can be changed, service crashes or stops
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-09-08 | CVE-2026-84869 published in NVD | NVD |
| 2026-09-11 | CVE-2026-84869 added to CISA KEV (actively exploited) | CISA KEV |
| 2026-09-14 | US federal agencies must patch by this date | CISA KEV |
| 2026-11-12 | Reported by The Hacker News | The Hacker News |
| 2026-11-12 | This Skillmate explainer published | Skillmate |
How to fix it
- Update ConnectWise ScreenConnect to the fixed release named in the vendor advisory.
- Read the vendor advisory for CVE-2026-84869 and upgrade to the fixed release it lists.
- CVE-2026-84869 is in CISA KEV: treat it as actively exploited and patch first.
- If you cannot patch today, limit who can reach the affected service and watch its logs.
How to detect it
Defenders should look for unusual file transfers or command executions during remote sessions.
What is confirmed
- CVE-2026-84869 is a real NVD record scored 9.9 CRITICAL
- CISA lists CVE-2026-84869 as exploited in the wild
- Reported by The Hacker News
- Reported by www.connectwise.com
Why it matters
It affects companies and users globally, especially those using ScreenConnect for remote support.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What is CVE-2026-84869?
It's a security flaw in ScreenConnect that allows files to be transferred and executed without permission during a remote session.
What is SCKit malware?
SCKit is a malware that uses ScreenConnect's legitimate features to hijack operator sessions and spread malicious code.
How many partner environments were affected?
Approximately 400 partner environments with third-party extensions from the RMM+ family were identified.
What should partners do?
Partners should disable the third-party extensions and investigate their environments for any unauthorized activity.
Related Skillmate posts
Sources
- SCKit Malware Turns ScreenConnect Support Sessions Into Potential MSP Attack Paths (The Hacker News)
- Vendor advisory CVE-2026-84869 (www.connectwise.com)
- NVD CVE record (NVD)
How we wrote this: facts come from the sources above, NVD and CISA KEV. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.