
Short answer: AI-related hacks hit WorkOS, Northflank, and Trigger.dev. Customer data might be exposed. Rotate API keys and third-party credentials.
TL;DR
- Hacks used AI tools to speed up attacks.
- Customers affected by WorkOS should review data.
- WorkOS disabled access to the affected application.
- Rotate credentials if notified.
What happened at WorkOS?
AI-related hacks involved attackers using AI tools to breach platforms like WorkOS, Northflank, and Trigger.dev. These attacks aim to steal API keys and tokens to access customer data. WorkOS notified customers and disabled access to the affected application. The main risk is rotating credentials and reviewing data access.
- Data breach
- When private information is stolen or exposed to people who should not see it.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | SecurityWeek |
|---|---|
| Date reported | 04 Nov 2026 |
How it works
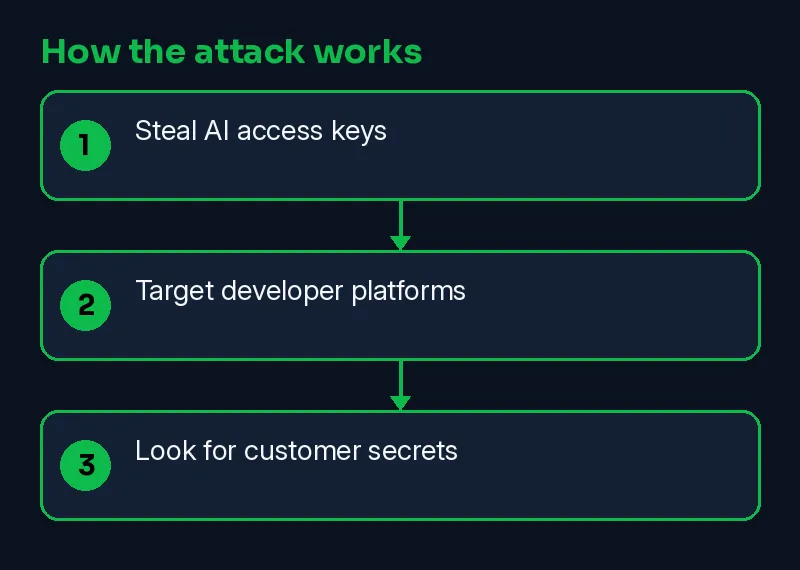
Hackers steal AI access keys to sell them and use AI tools to quickly break into systems. They target developer platforms, looking for customer secrets, especially credentials. This lets them access sensitive information and make attacks more effective.
- Steal AI access keys
- Target developer platforms
- Look for customer secrets
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-04 | Reported by SecurityWeek | SecurityWeek |
| 2026-11-09 | This Skillmate explainer published | Skillmate |
How to fix it
- If you have an account with the affected company, change that password and any reused copies of it.
- Turn on two-factor authentication (a second login step) wherever the service offers it.
- Expect phishing emails or calls that use the exposed details; verify requests through official channels.
How to detect it
Look for unusual login attempts, sudden crashes, and unexpected logs. A false positive might be a routine update causing a system crash.
Signs to watch for:
- Login alerts from new devices or locations on the affected account.
- Password-reset emails you did not ask for.
- Phishing messages that quote your real account details.
What is confirmed
- Reported by SecurityWeek
- Reported by fireworks.ai
- Reported by workos.com
Why it matters
This matters because hackers can steal sensitive information and make attacks more effective. Companies need to secure their credentials and secrets to protect customer data and systems. Students should learn about these threats to better prepare for cybersecurity challenges.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
How can I protect against AI-assisted attacks?
Regularly review access controls and monitor for unusual activity. Verify requests before sharing sensitive information.
What happened in the WorkOS incident?
Unauthorized access was found in an internal tool used by sales teams. Business contact details and customer communications were accessed.
Are these attacks related?
The incidents seem part of a wider trend of attacks using AI tools, but they are not directly linked.
Sources
- AI-Linked Breaches Mount as WorkOS, Northflank, Trigger.dev Disclose Hacks (SecurityWeek)
- Primary source / advisory (fireworks.ai)
- Primary source / advisory (workos.com)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.