
Short answer: A school in the UK was attacked by 3AM ransomware, with a hybrid human-AI method. Machines were encrypted and trust built between domains. To defend, update systems, use EDR, and train staff.
TL;DR
- 3AM ransomware used human-AI hybrid
- Encrypted 37 machines, built trust
- Update systems, use EDR, train staff
What happened?
3AM ransomware attacked a UK school using a mix of human and AI techniques. The attackers encrypted 37 machines and built trust between different domains. This shows how attackers are combining human and AI to make their attacks more effective. To protect against such attacks, keep systems updated, use endpoint detection and response tools, and train staff to recognize and respond to threats.
- Ransomware
- Malware that locks or steals files and demands money to give them back.
- Credentials / secrets
- Passwords, keys and tokens that prove who you are to a system.
Key facts
| Reported by | Infosecurity Magazine |
|---|---|
| Date reported | 04 Nov 2026 |
How it works
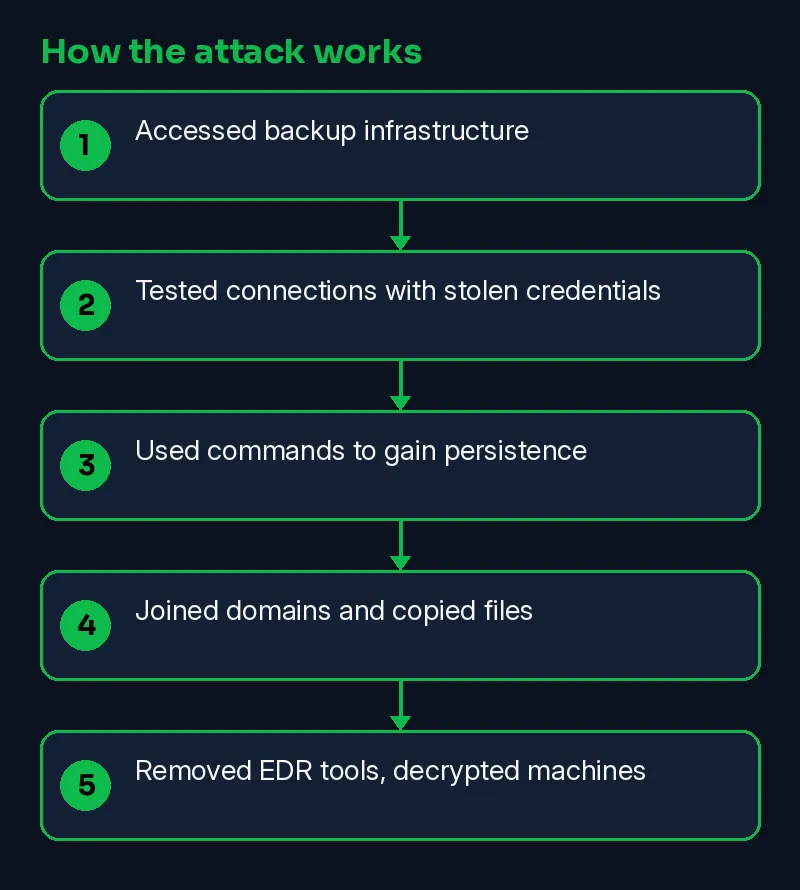
A UK school was attacked by 3AM ransomware. First, attackers used stolen credentials. Then, they tested connections and used commands. Later, they joined different domains and copied files. Finally, they removed EDR tools and decrypted machines.
- Accessed backup infrastructure
- Tested connections with stolen credentials
- Used commands to gain persistence
- Joined domains and copied files
- Removed EDR tools, decrypted machines
Skillmate analyst mapping (our judgement, not from the vendor):
- T1486 Data Encrypted for Impact
Timeline
| Date | Event | Source |
|---|---|---|
| 2026-11-04 | Reported by Infosecurity Magazine | Infosecurity Magazine |
| 2026-11-10 | This Skillmate explainer published | Skillmate |
How to fix it
- Keep the operating system, browser and security software updated.
- Do not open unexpected attachments or install software from unofficial sources.
- Report suspicious files or pop-ups to your IT or security team.
How to detect it
Defenders should look for unusual logins, encrypted files, and domain trust issues.
Signs to watch for:
- Unknown programs starting at boot, or new scheduled tasks.
- Security software that was turned off without a reason.
- Unusual outbound connections from a workstation.
What is confirmed
- Reported by Infosecurity Magazine
Why it matters
This shows hybrid human-AI attacks are becoming common. Companies and users should prepare for such attacks, using strong credentials and EDR tools.
Learn the skills behind this story
Want to understand attacks like this and defend against them? Join Skillmate cybersecurity training or practise hands-on in Skillmate Labs.
FAQ
What are the signs of a hybrid AI ransomware attack?
Signs include unusual logins, encrypted files, and domain trust issues. A routine software update causing a temporary slowdown might be mistaken for an attack.
How can I tell if an attack is human-AI hybrid?
Look for a mix of complex and simple commands, with delays between commands. Commands might be repeated, then quickly changed, indicating AI involvement.
Related Skillmate posts
Sources
- 3AM Ransomware Used Human-AI Hybrid Tactics in UK School Estate Compromise (Infosecurity Magazine)
How we wrote this: facts come from the sources above. An on-prem AI model drafted the plain-English parts and every sentence was checked against the sources; unsupported sentences were removed. MITRE mapping is our own judgement.